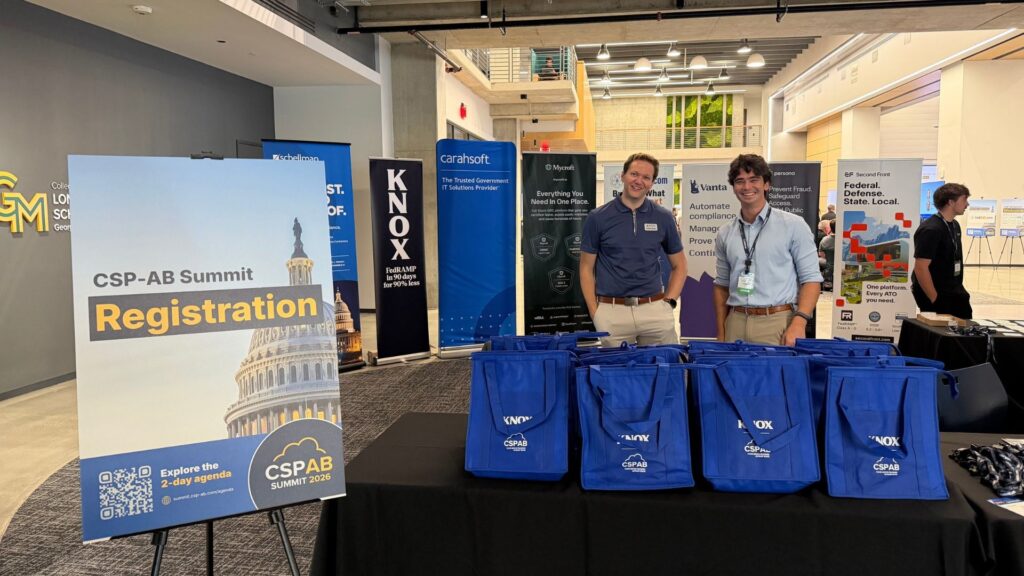
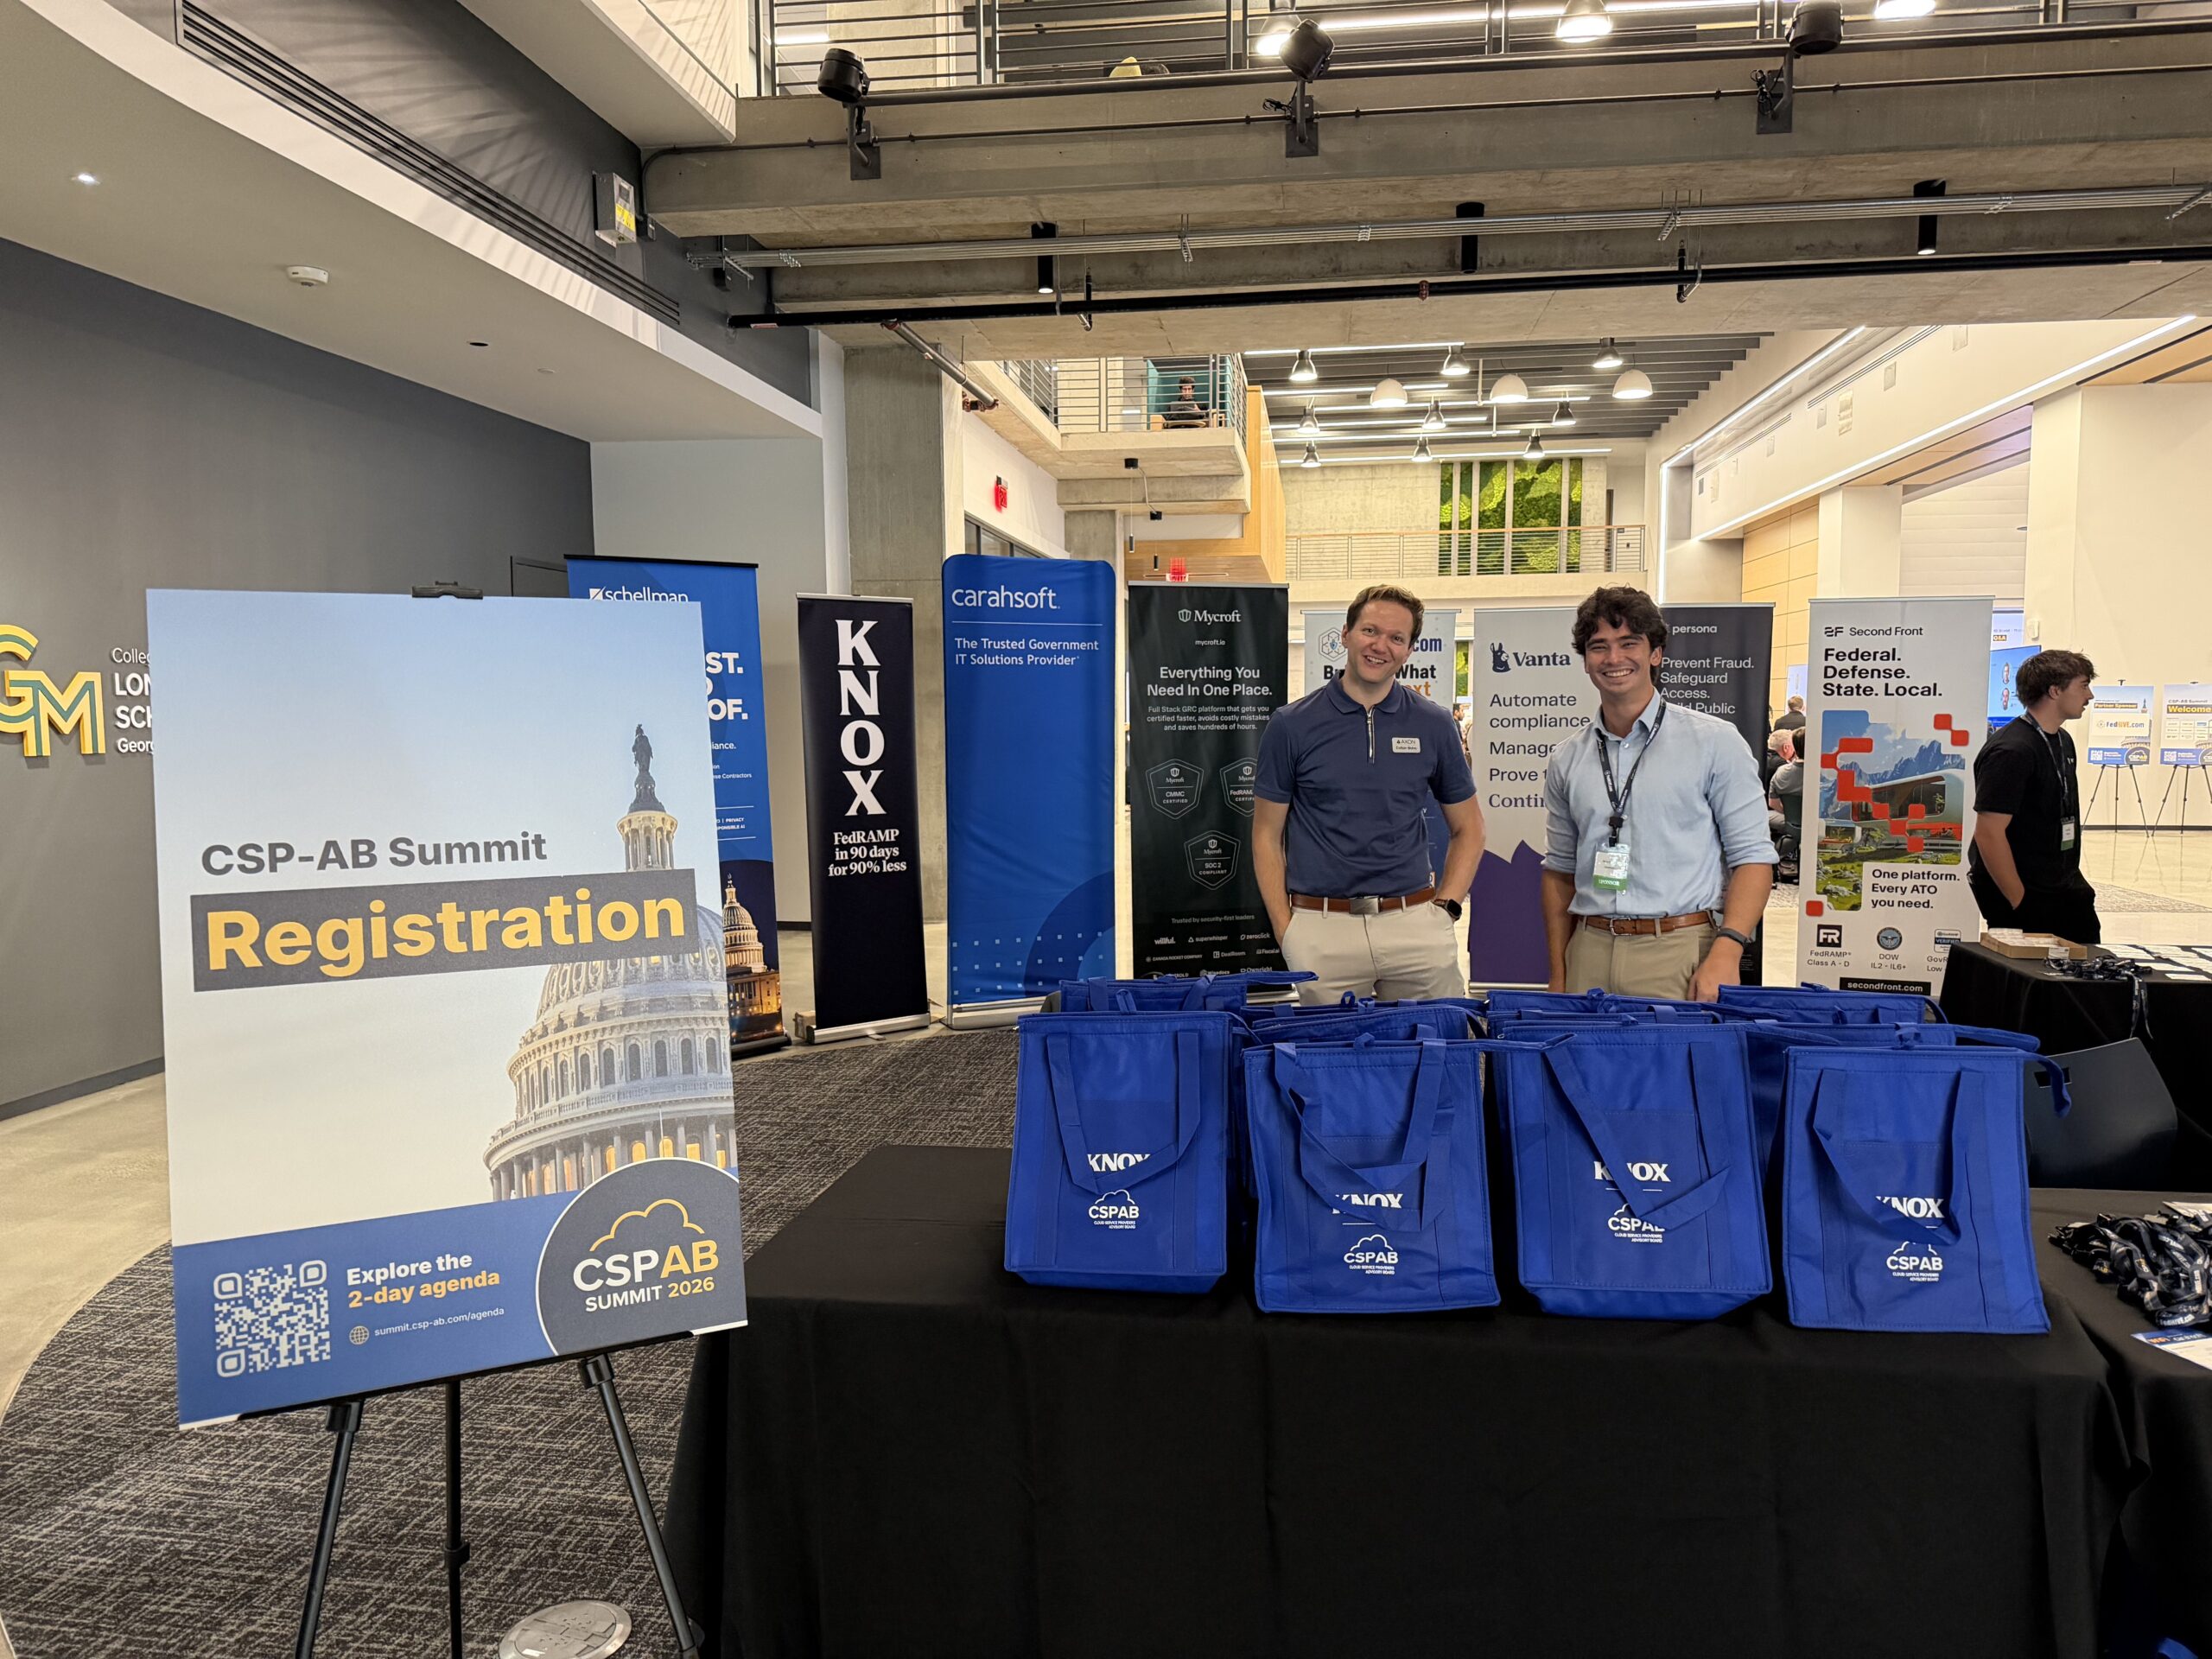
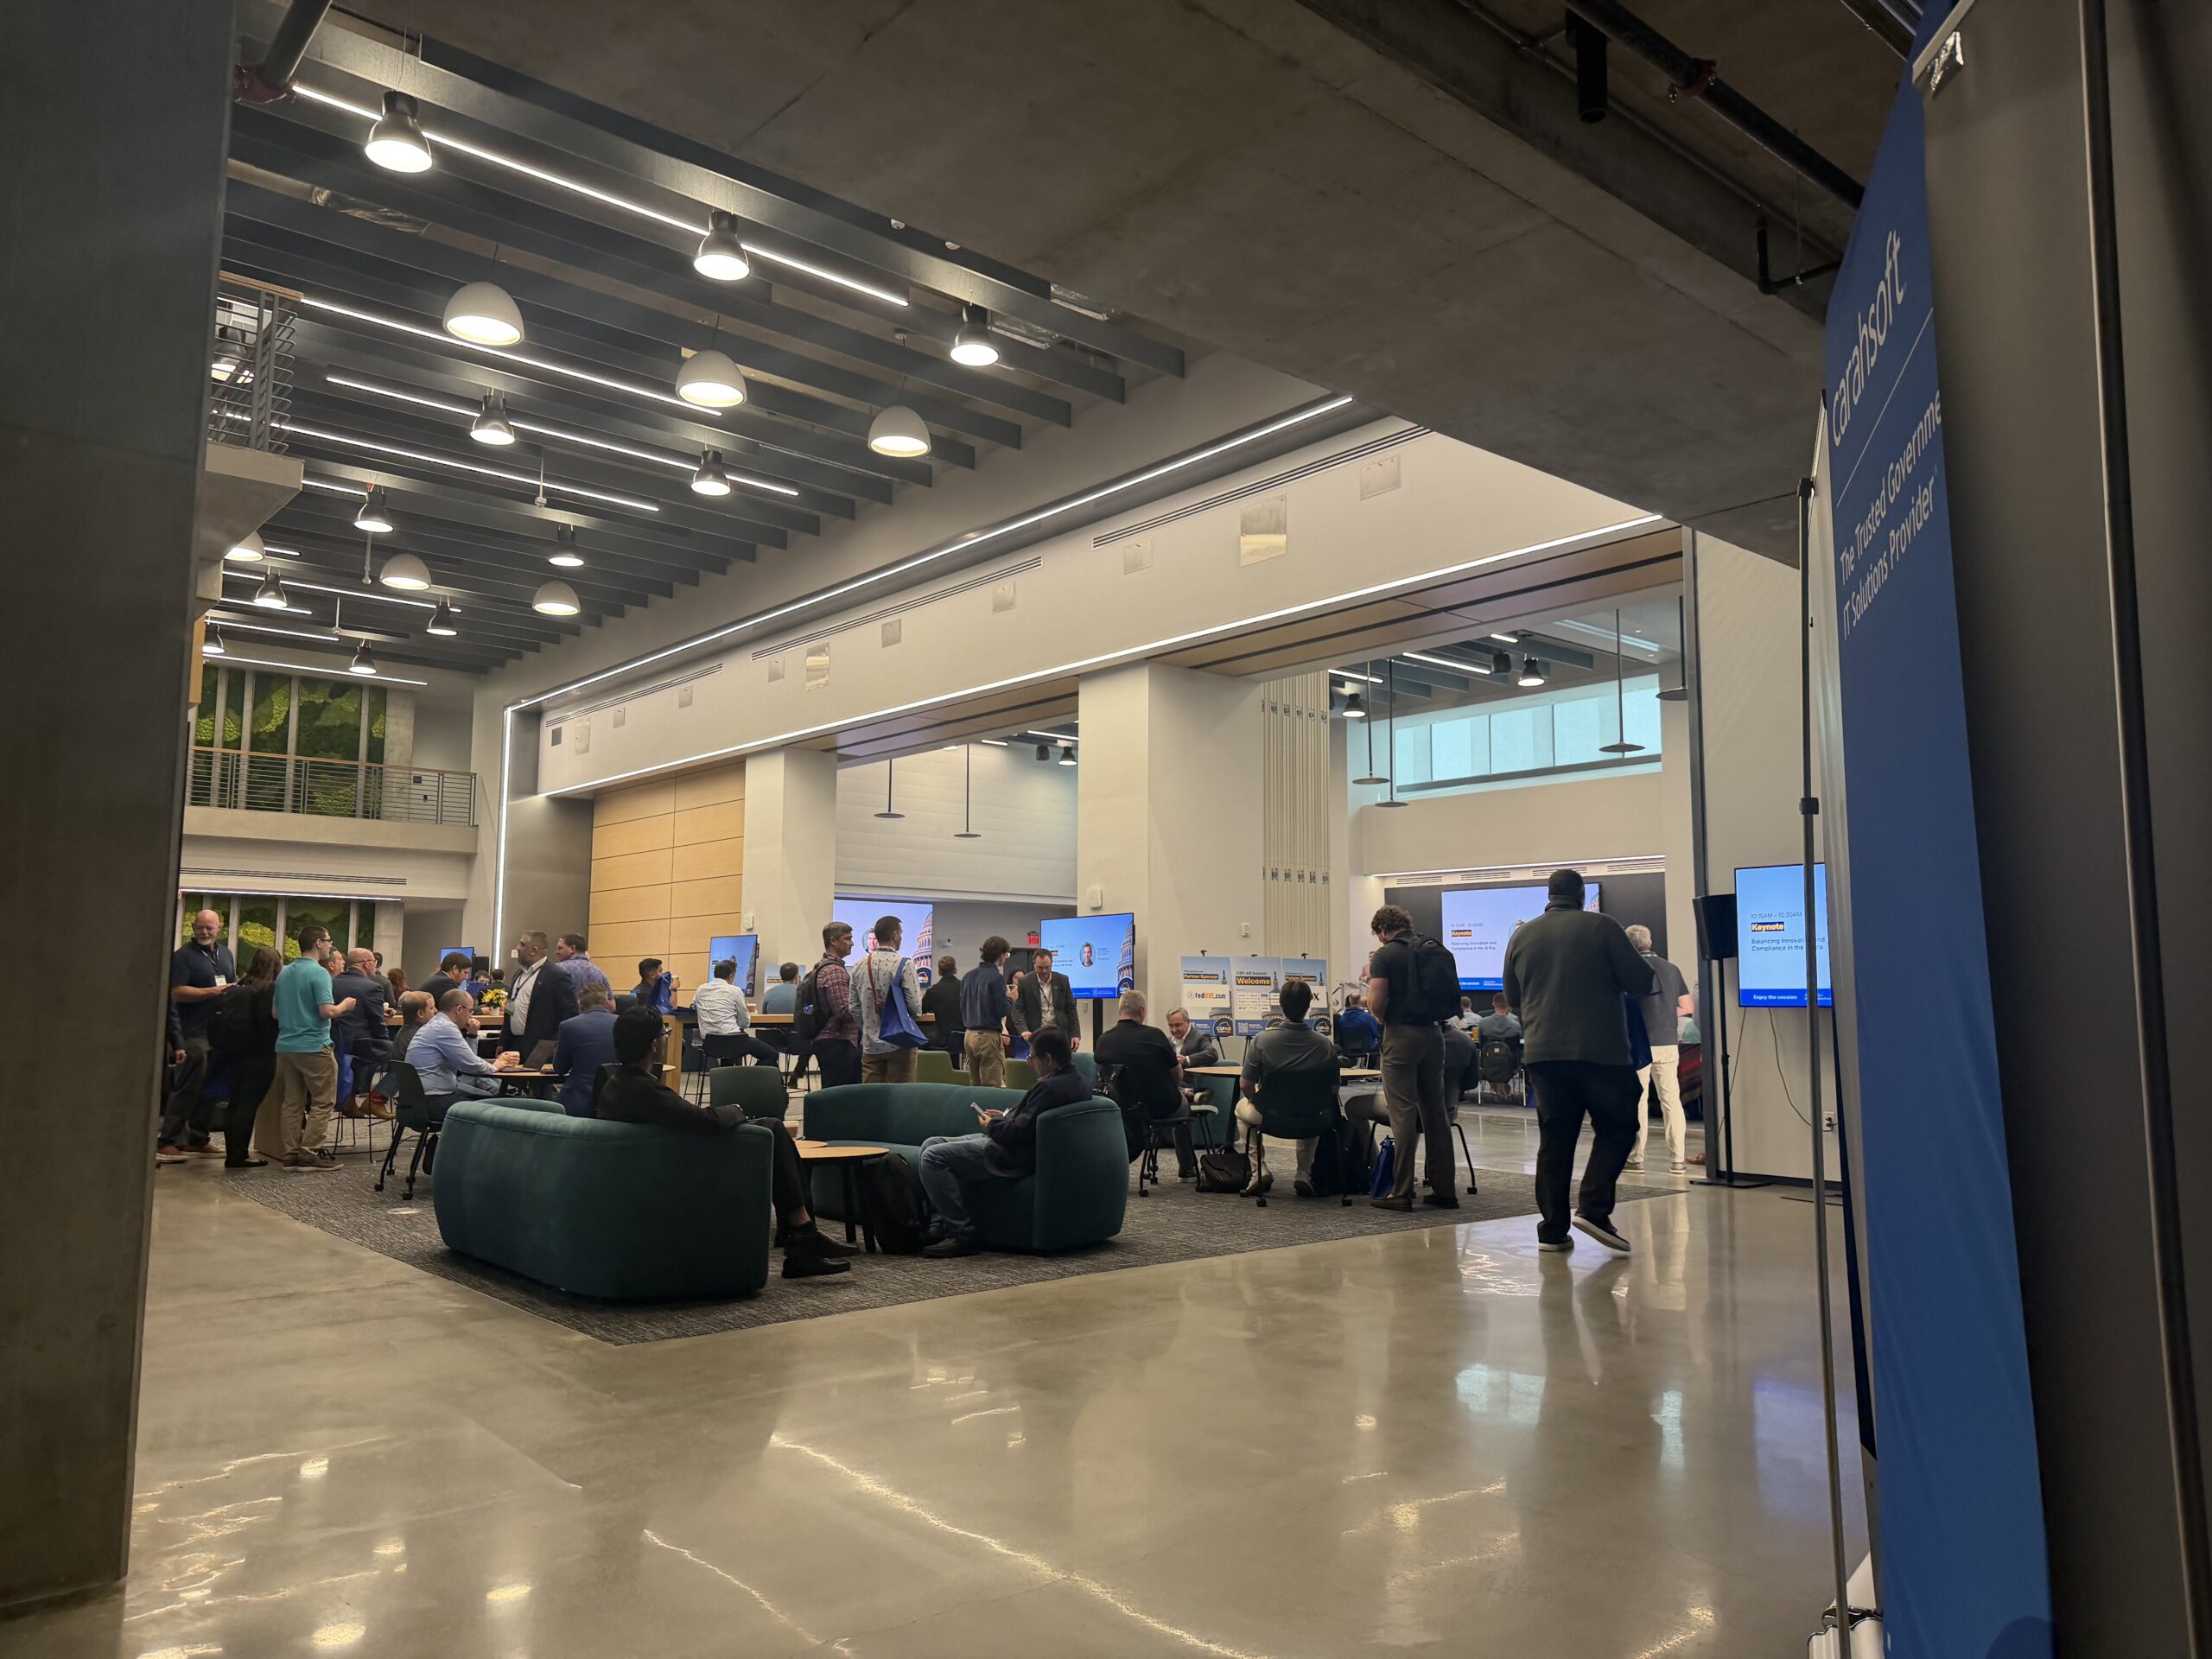
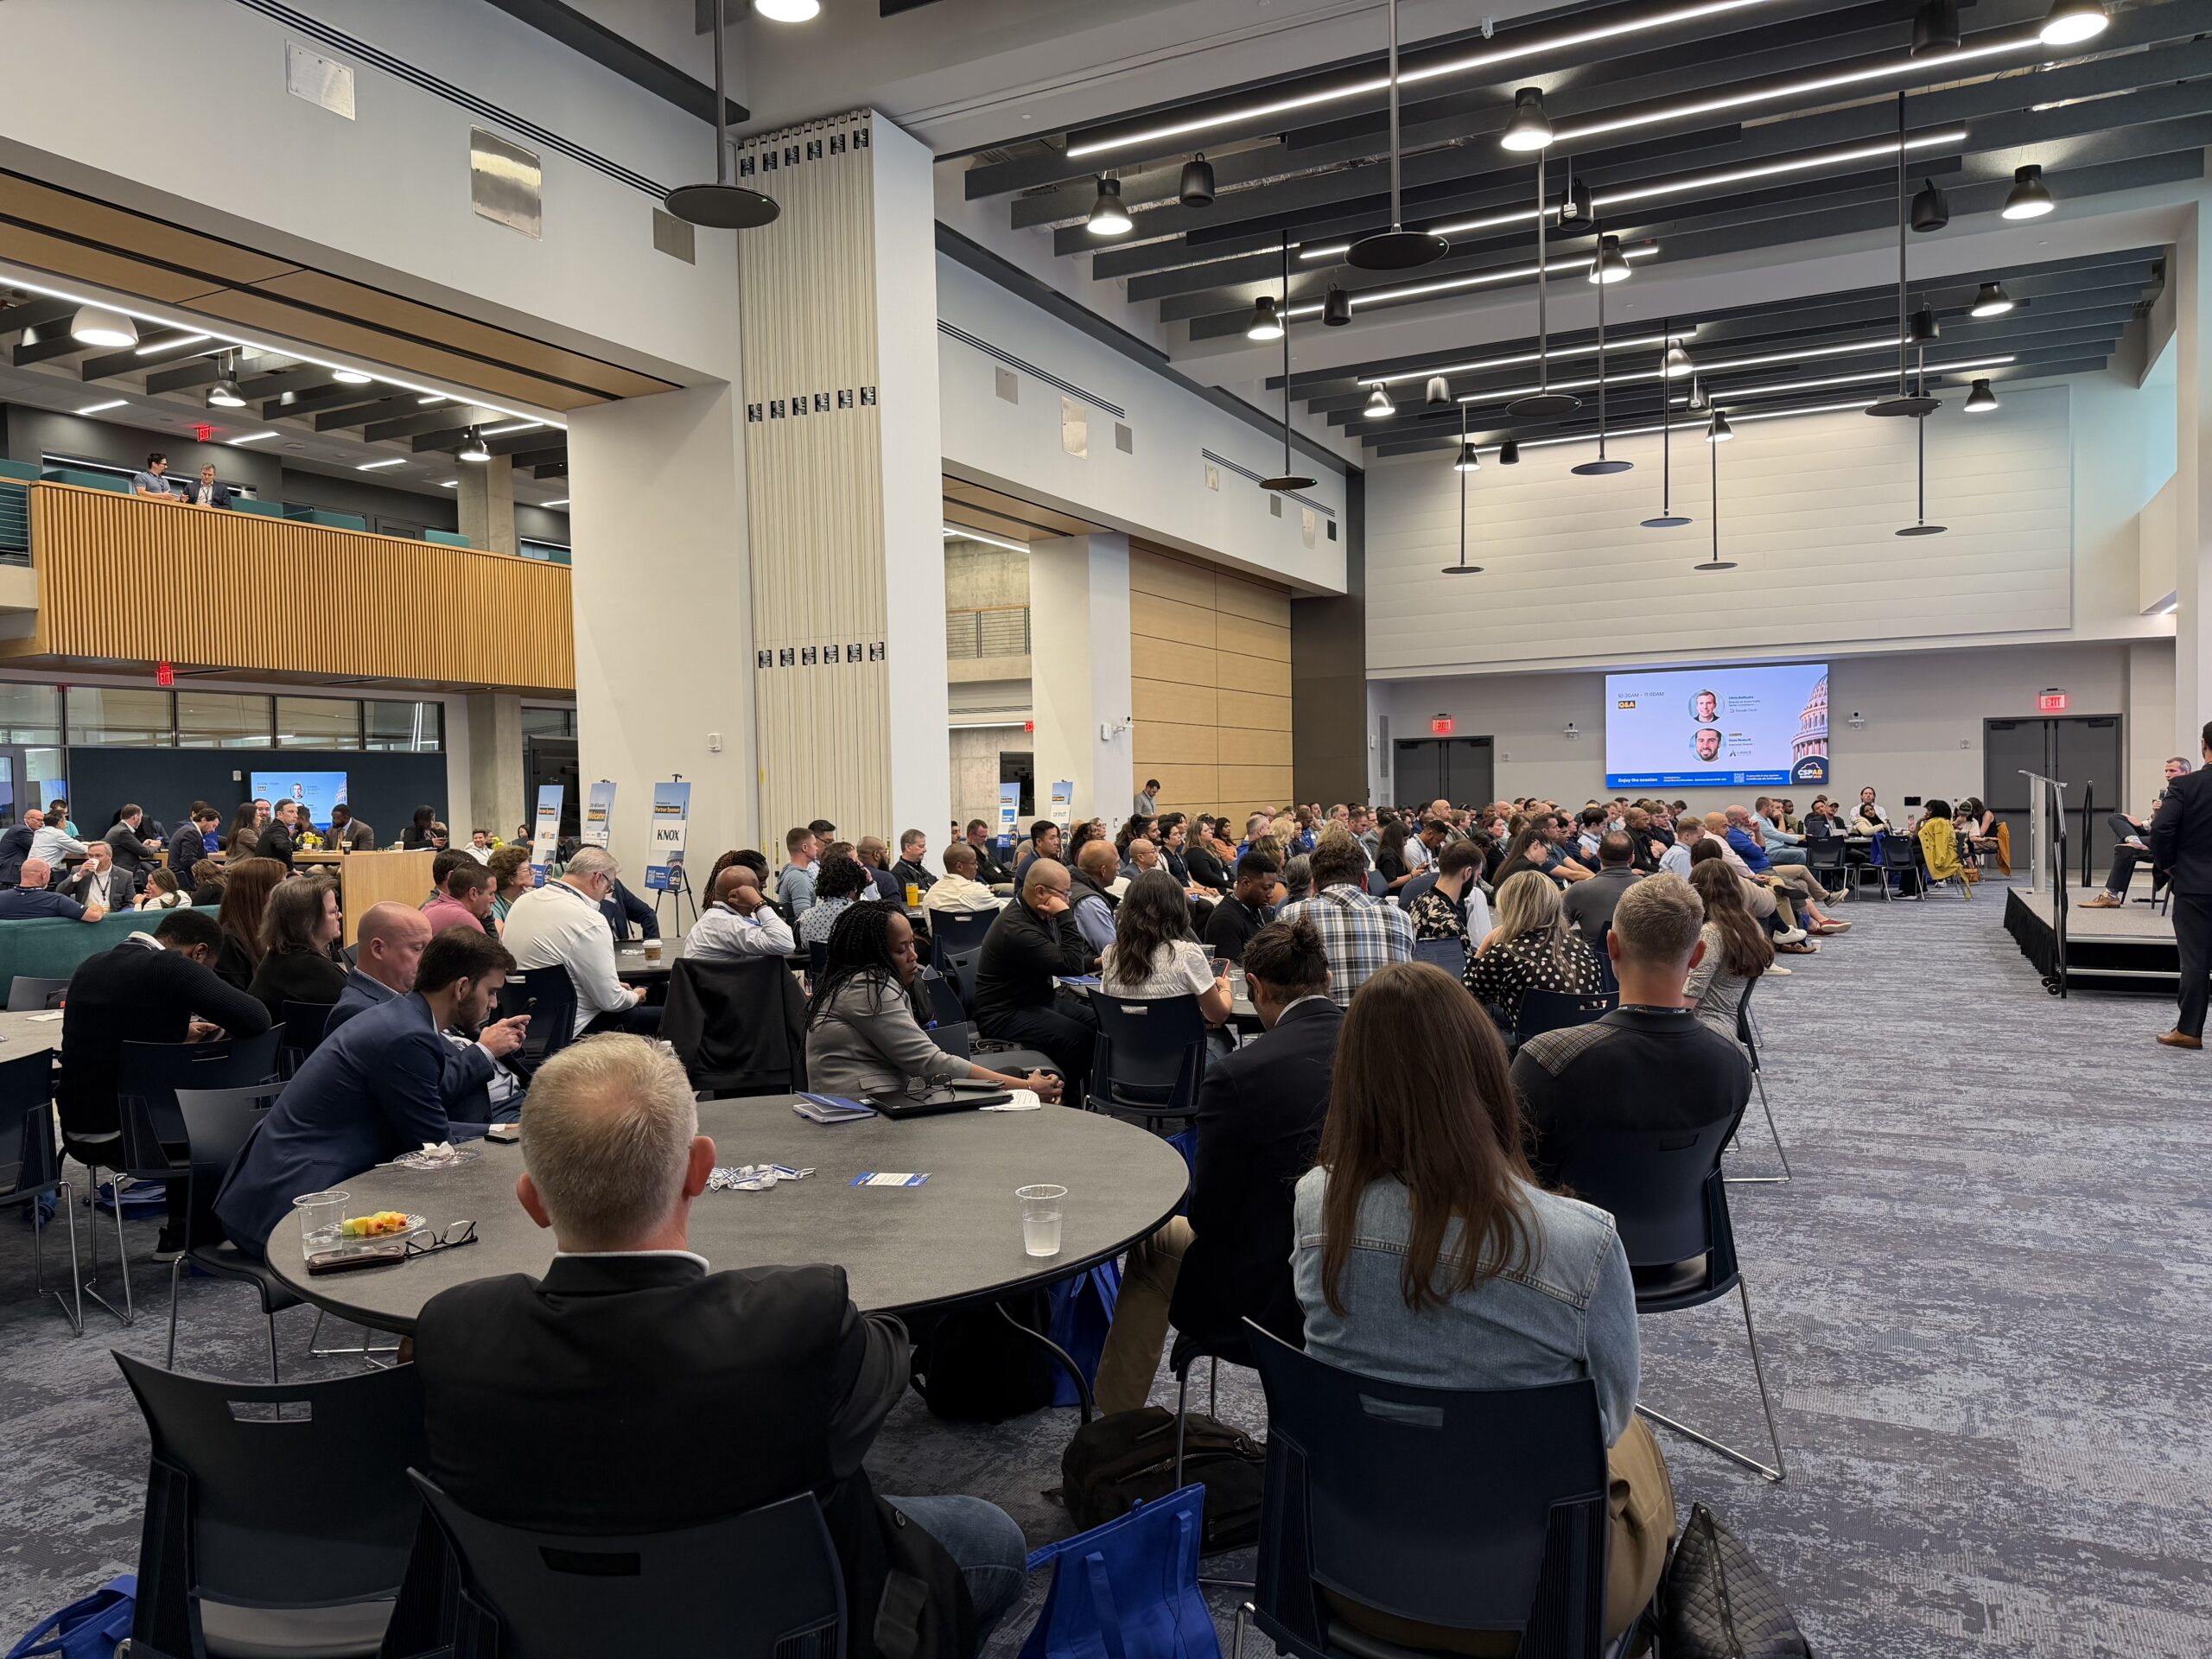
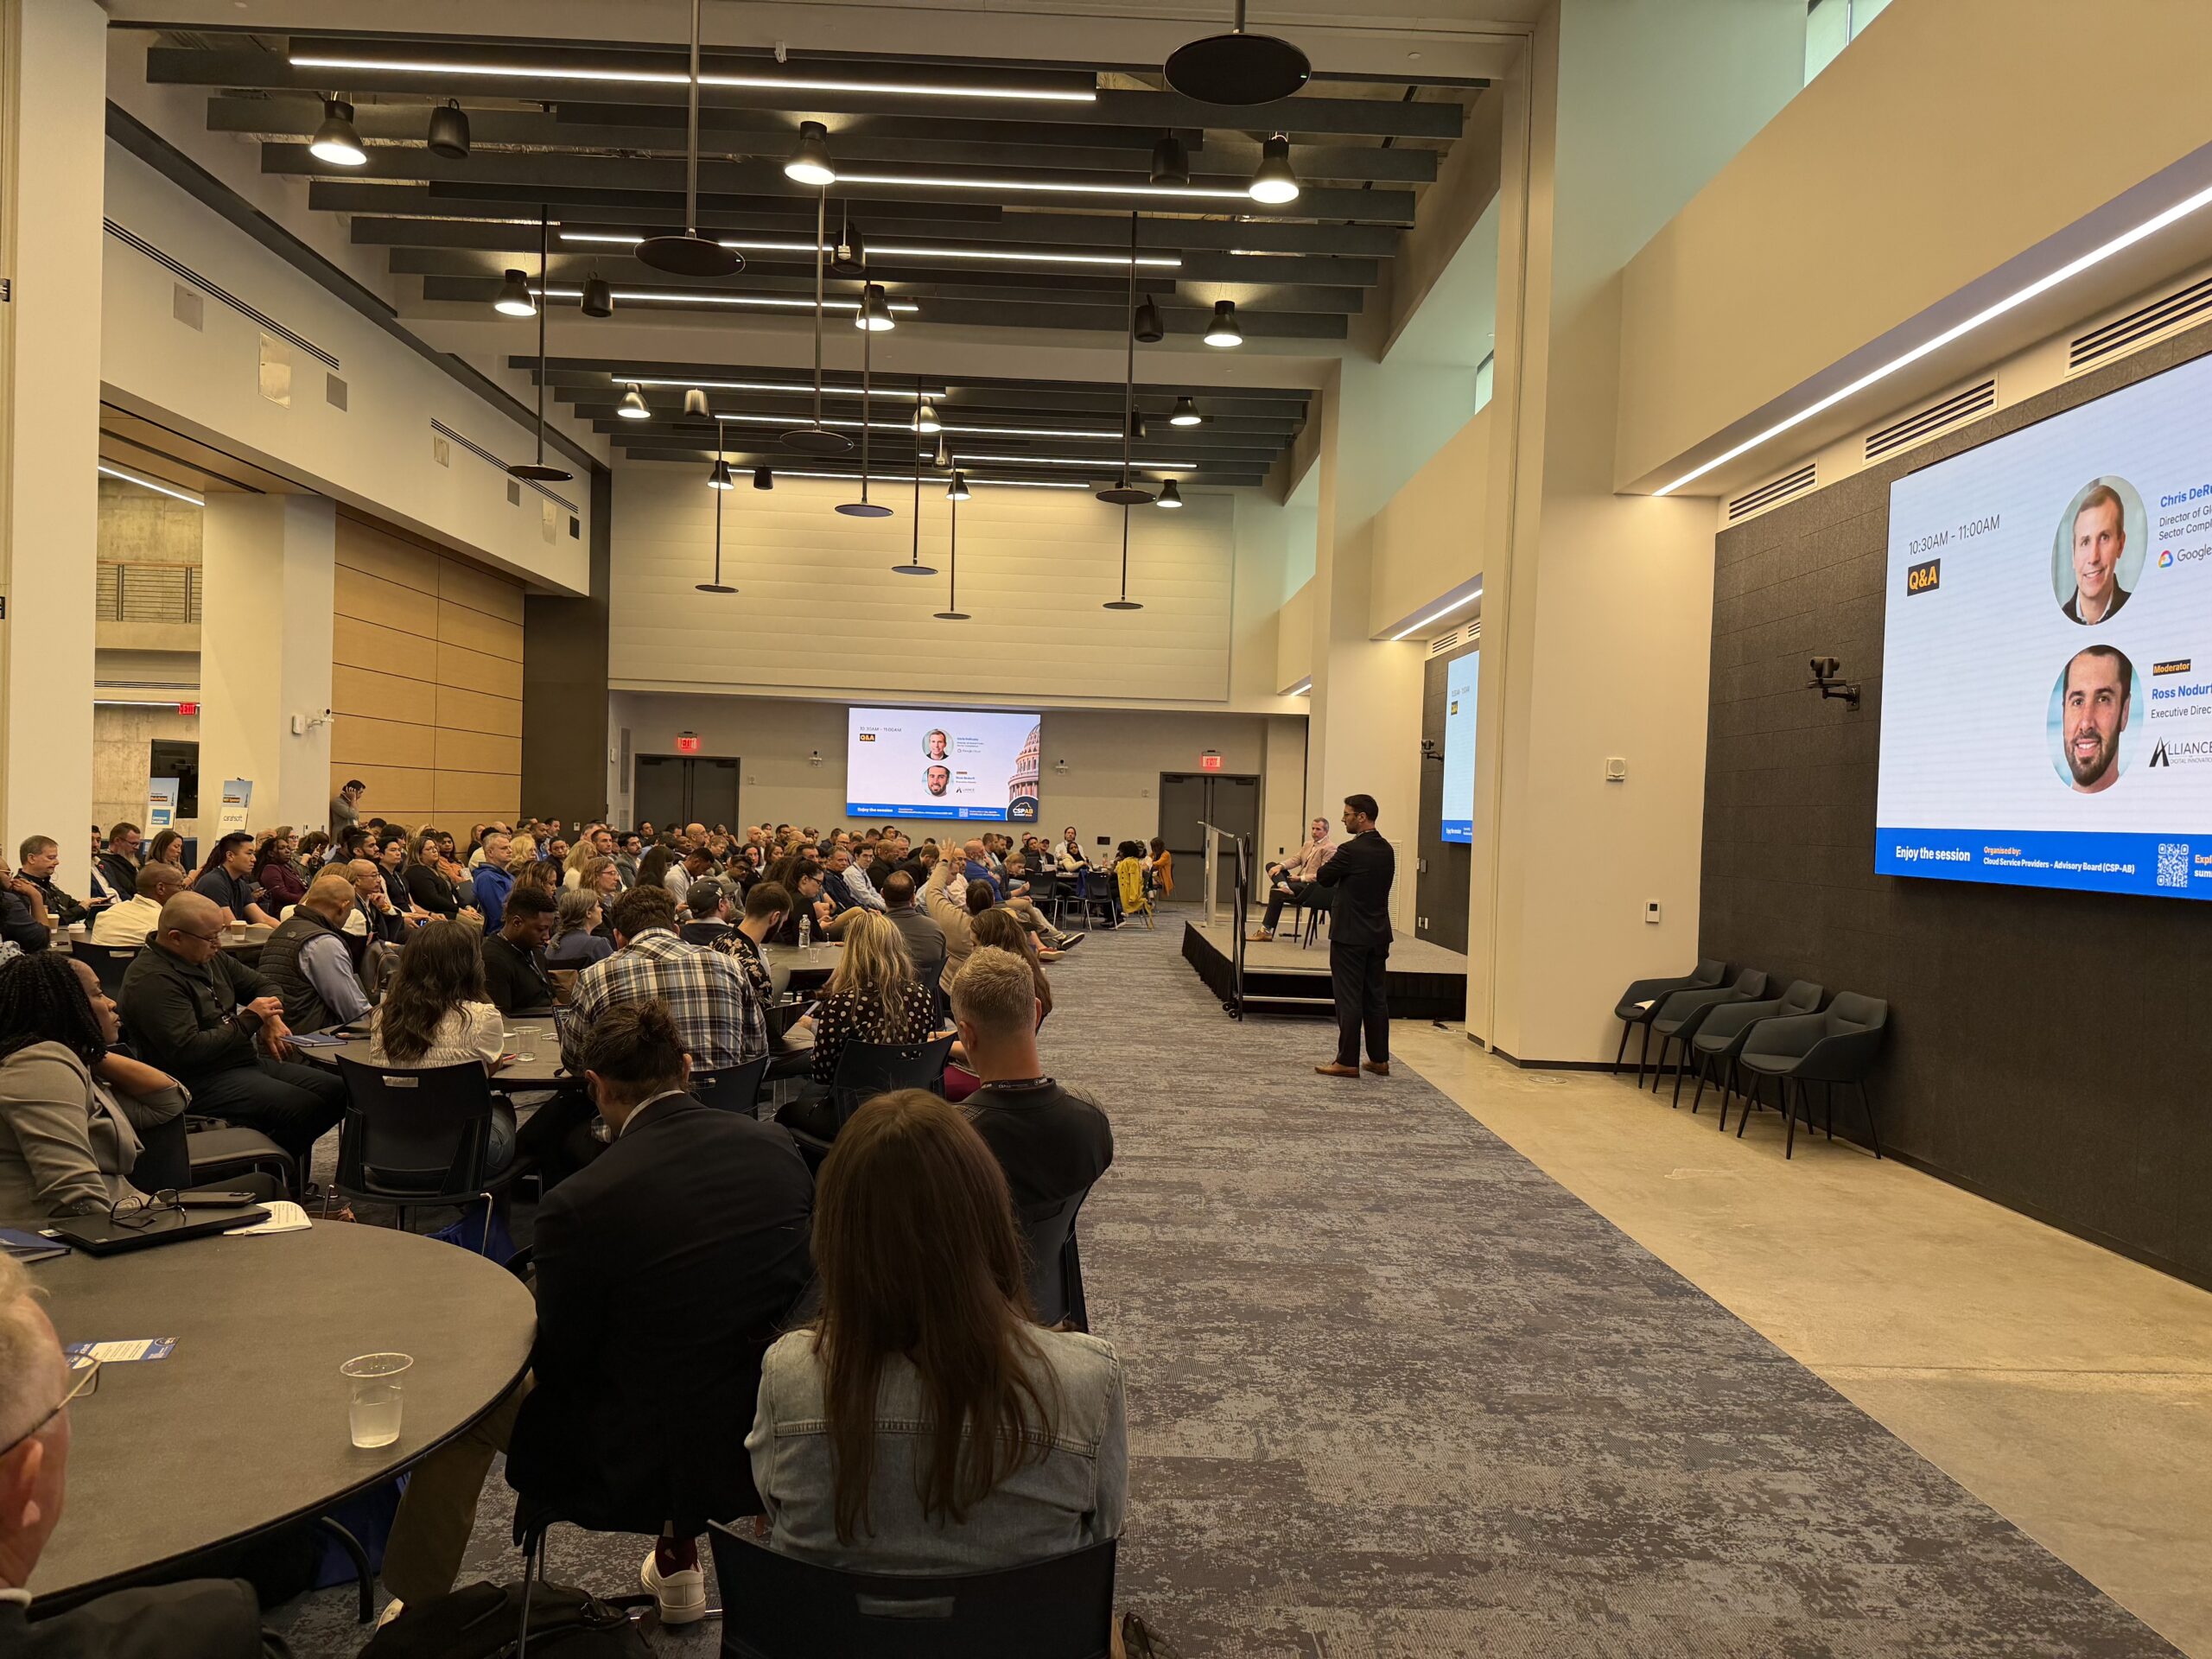
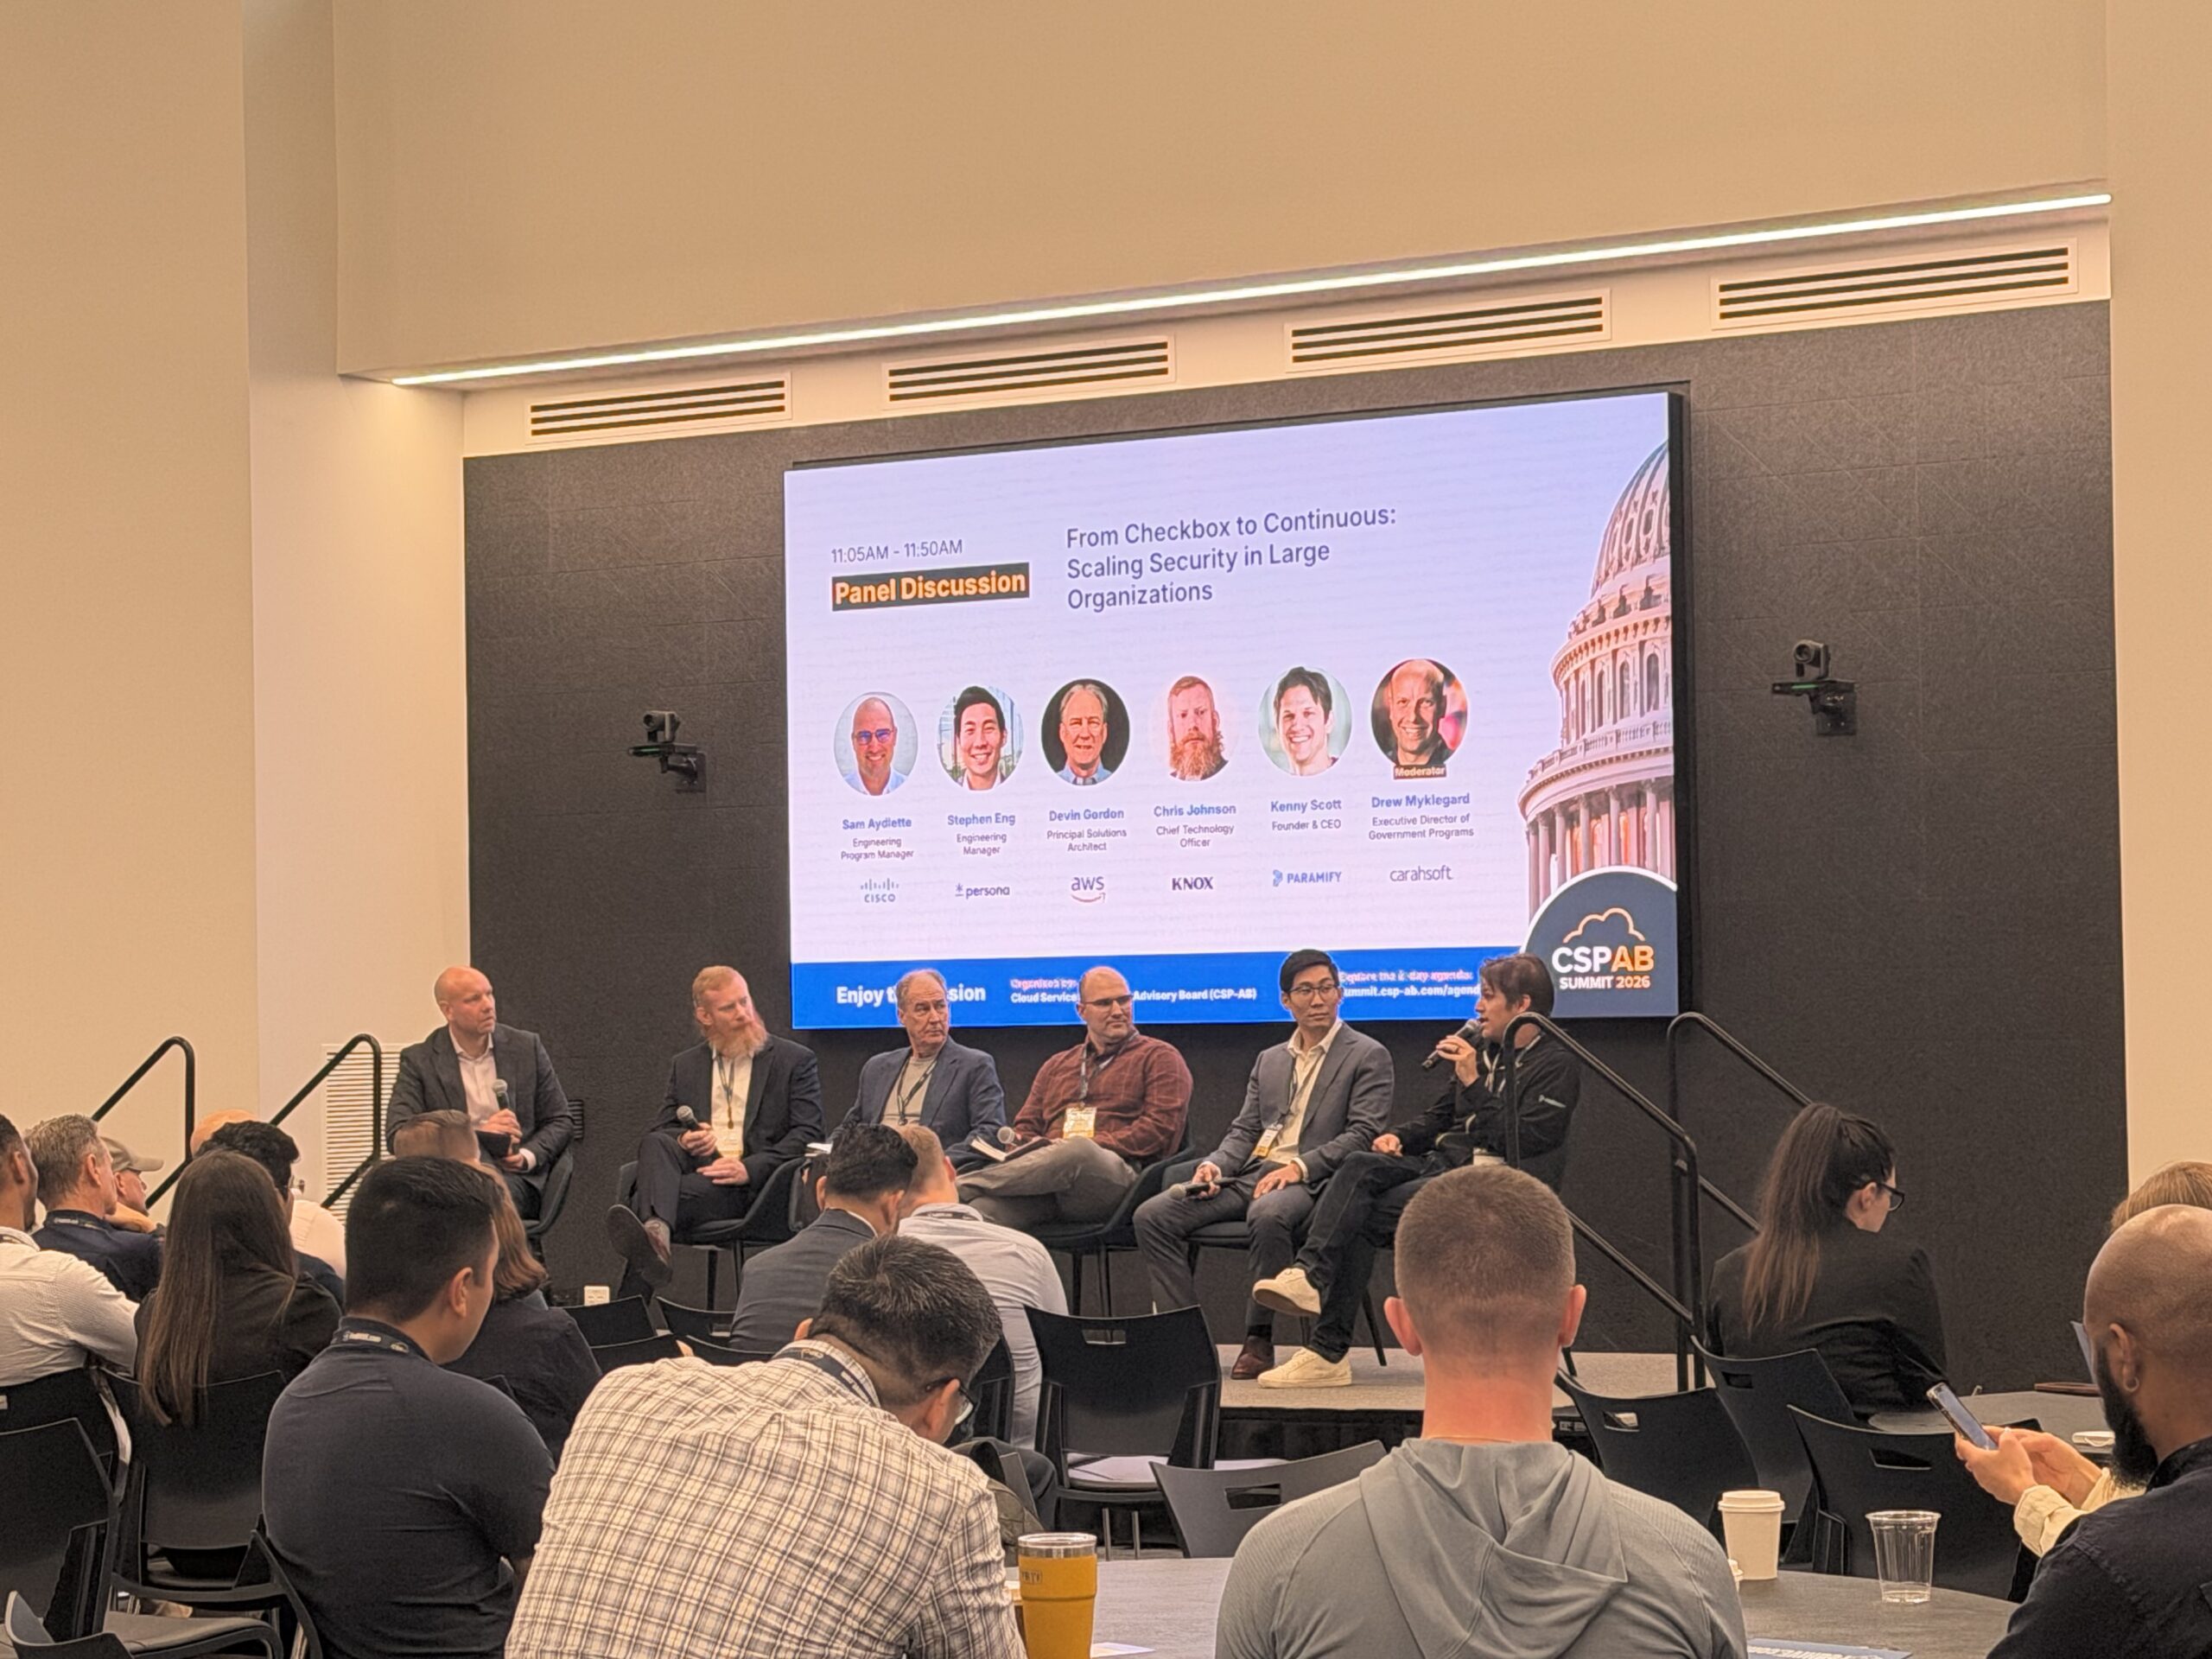
The Cloud Service Providers Advisory Board (CSP-AB) held its 2026 Summit on September 29–30 at Fuse at Mason Square in Arlington, Virginia. The event drew over 400 attendees from Federal agencies, cloud service providers, independent assessment organizations, and others in the cloud security community to discuss how Federal cloud security and compliance programs are changing.
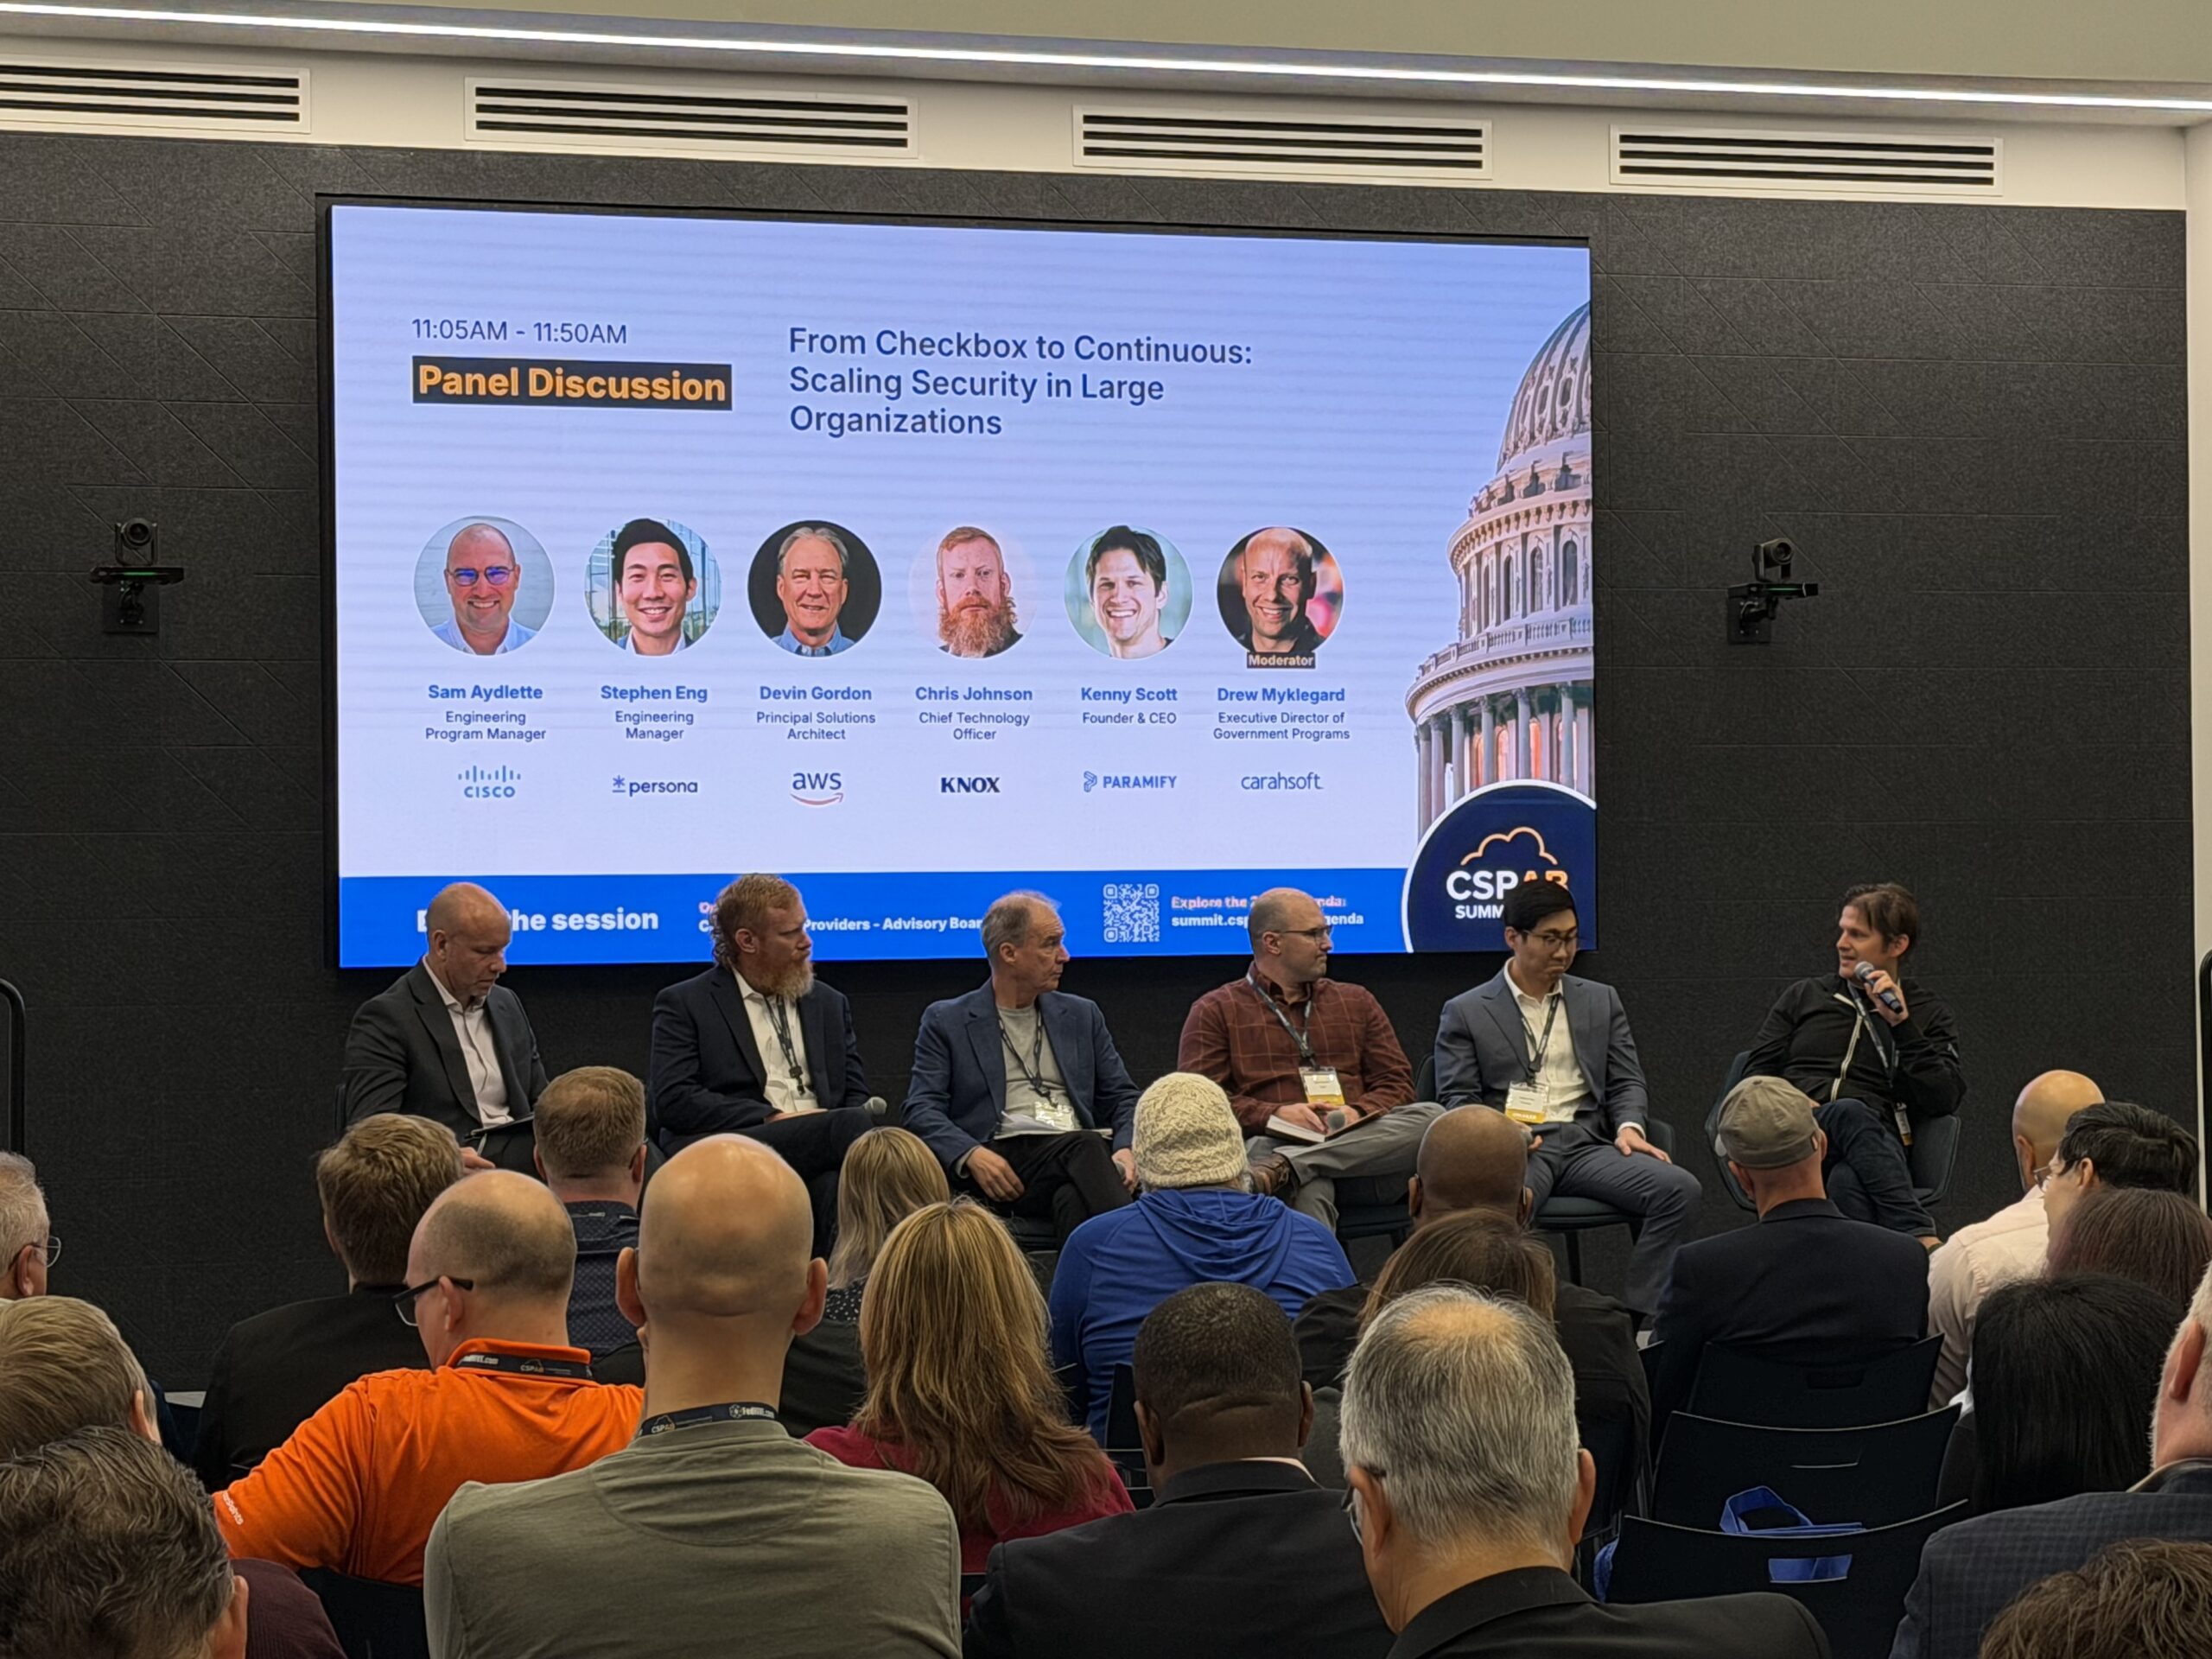
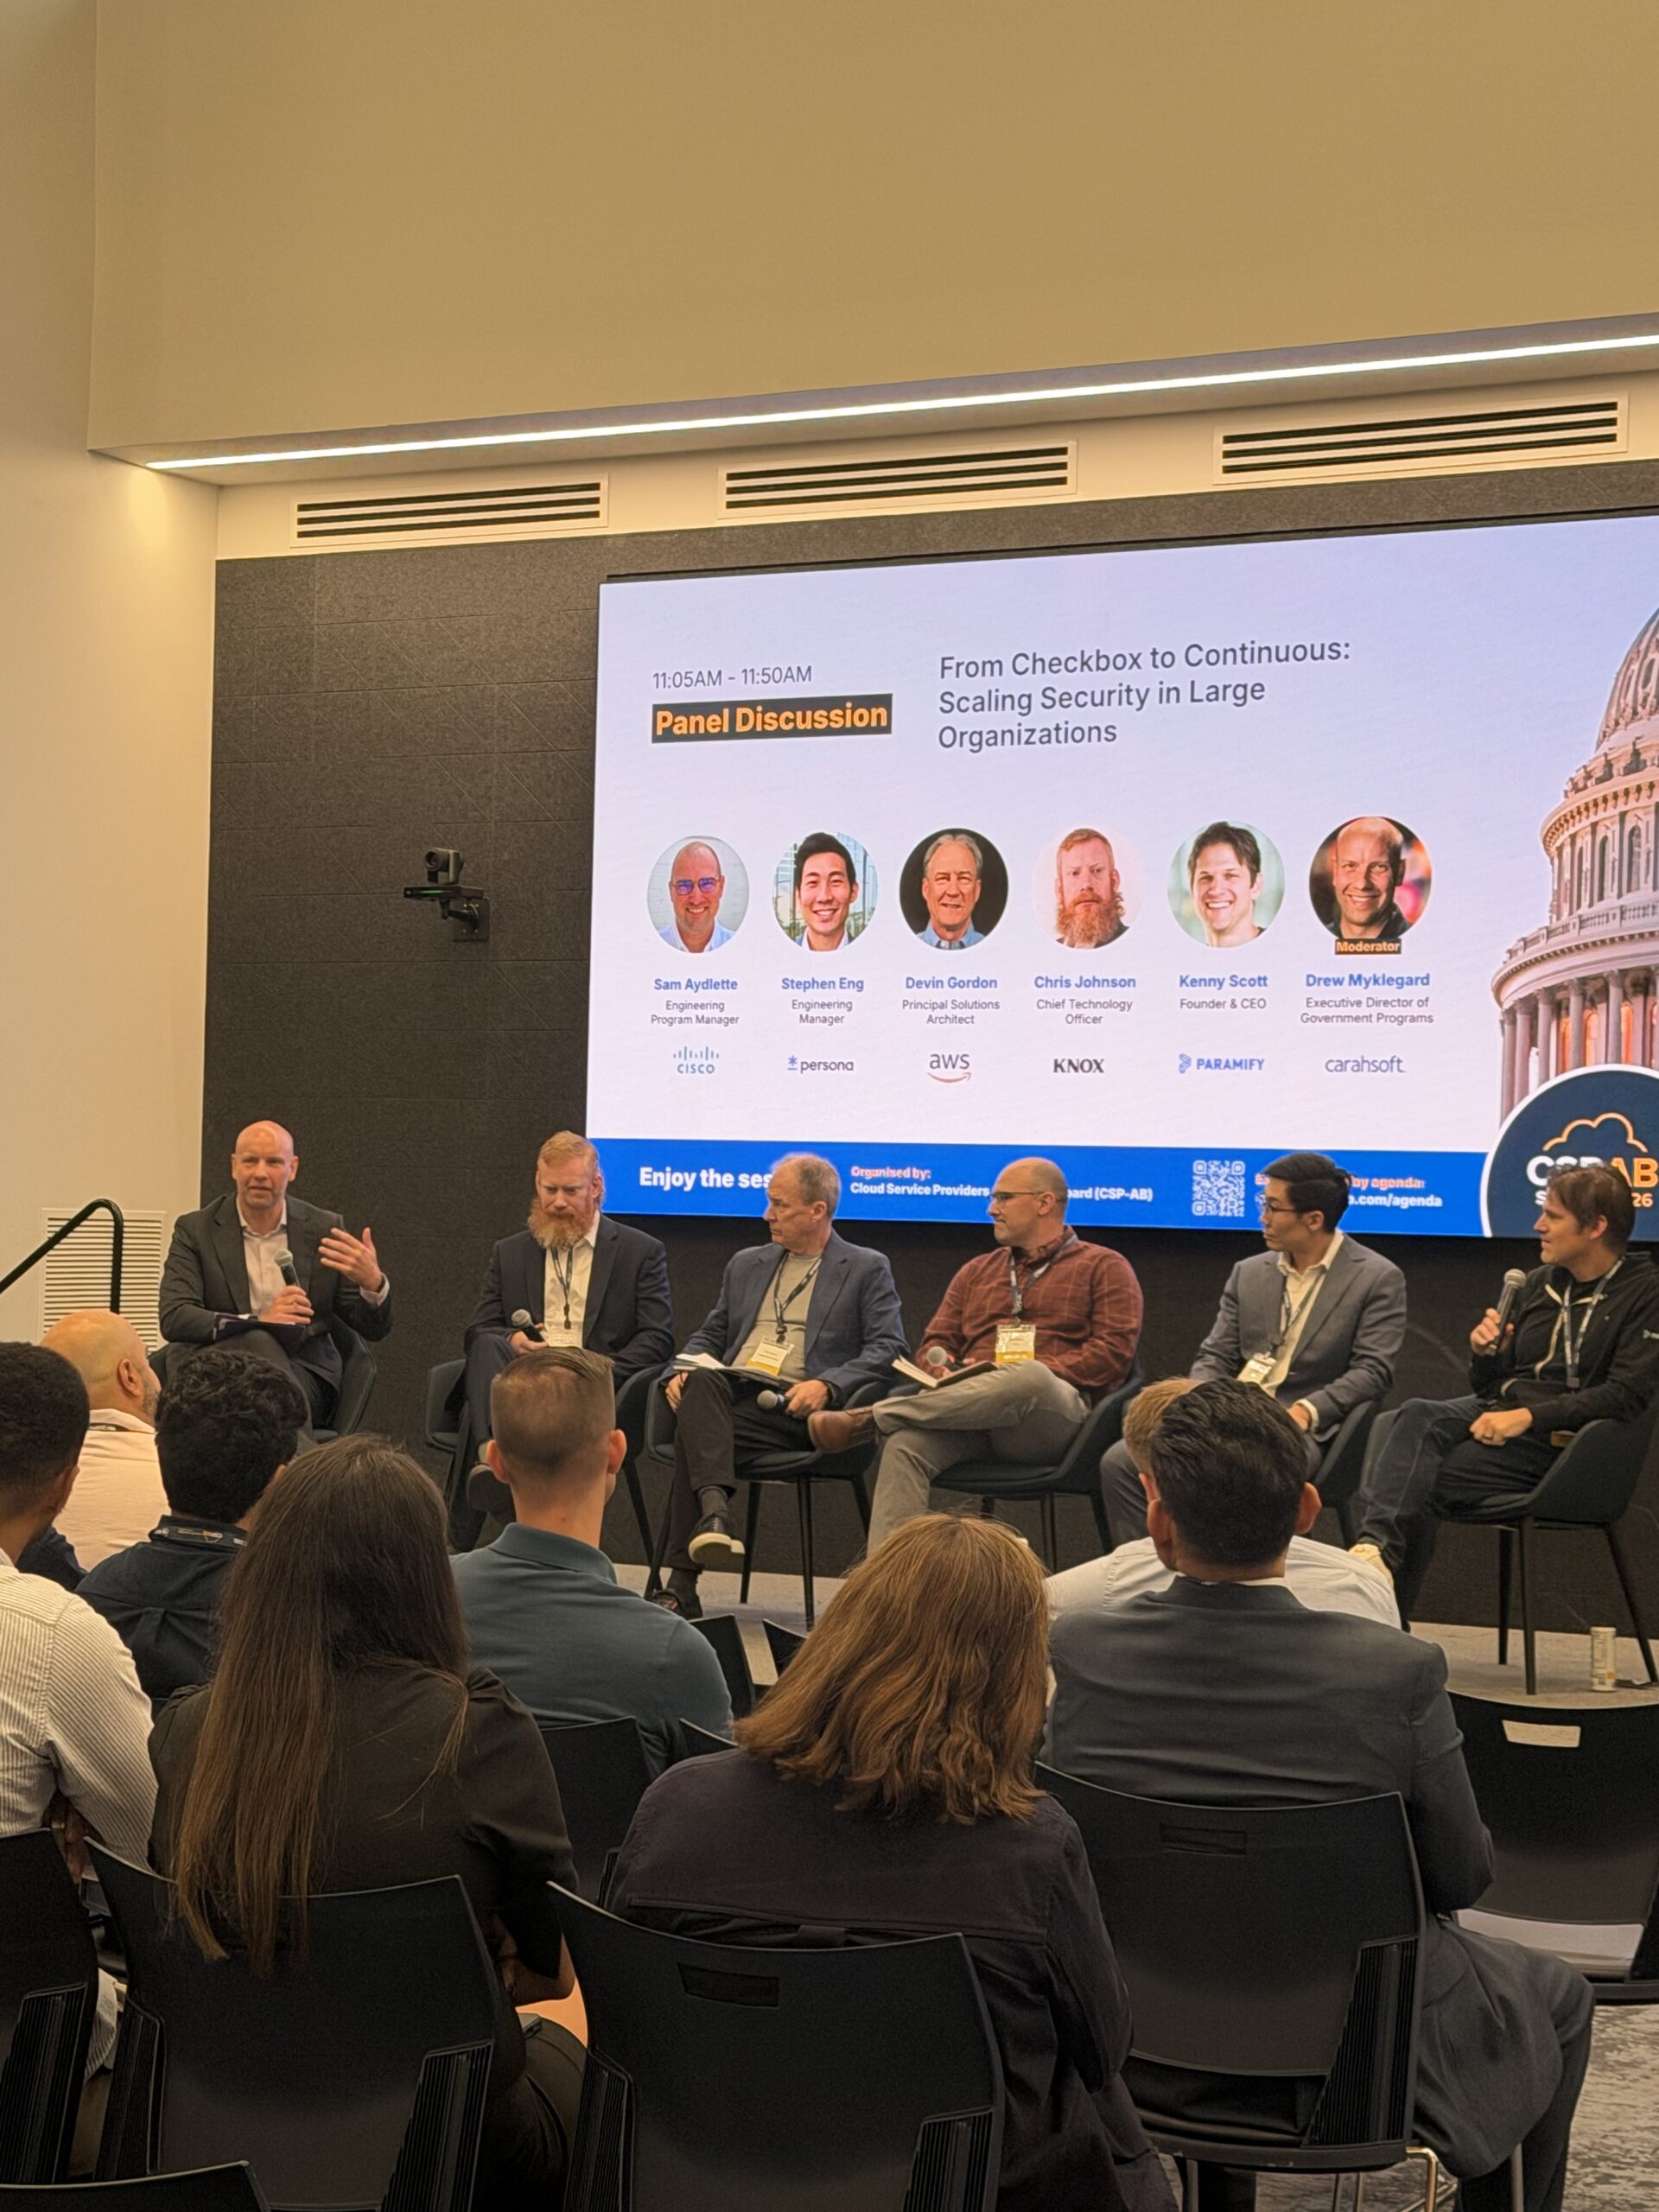
Day 1 focused on cloud security and ATO modernization. Sessions covered continuous security at scale, GRC tooling, and regulatory harmonization.
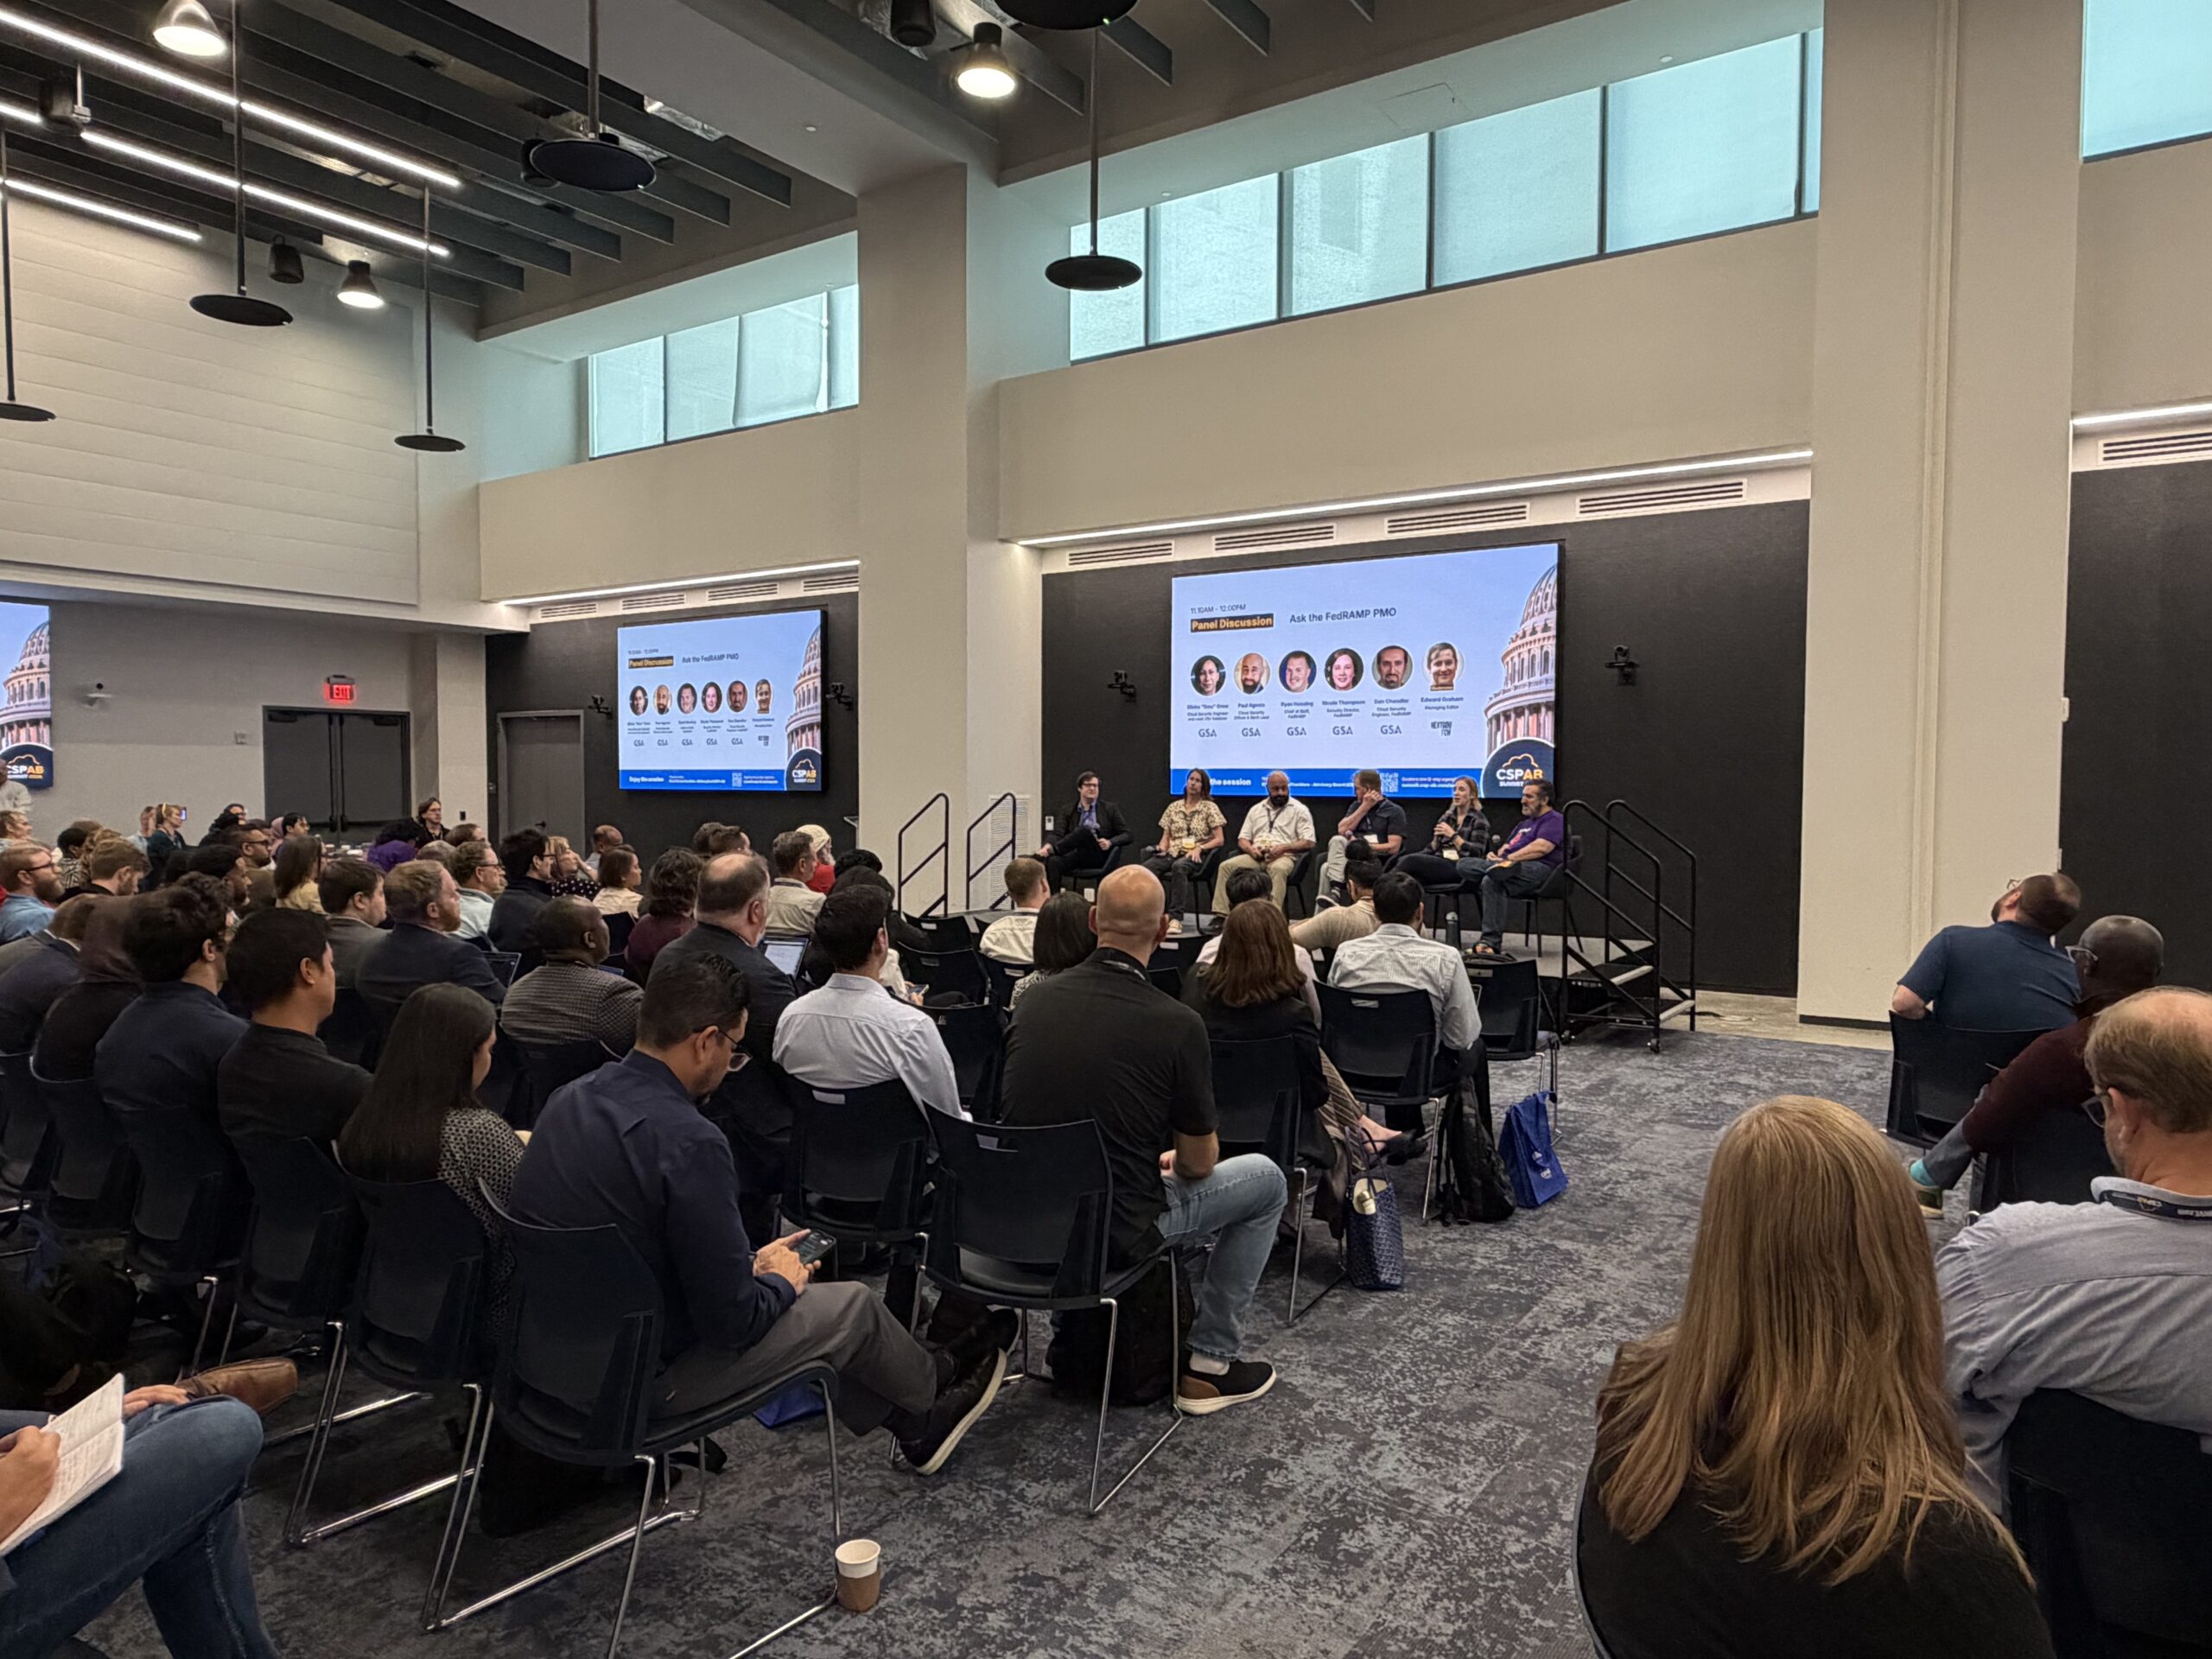
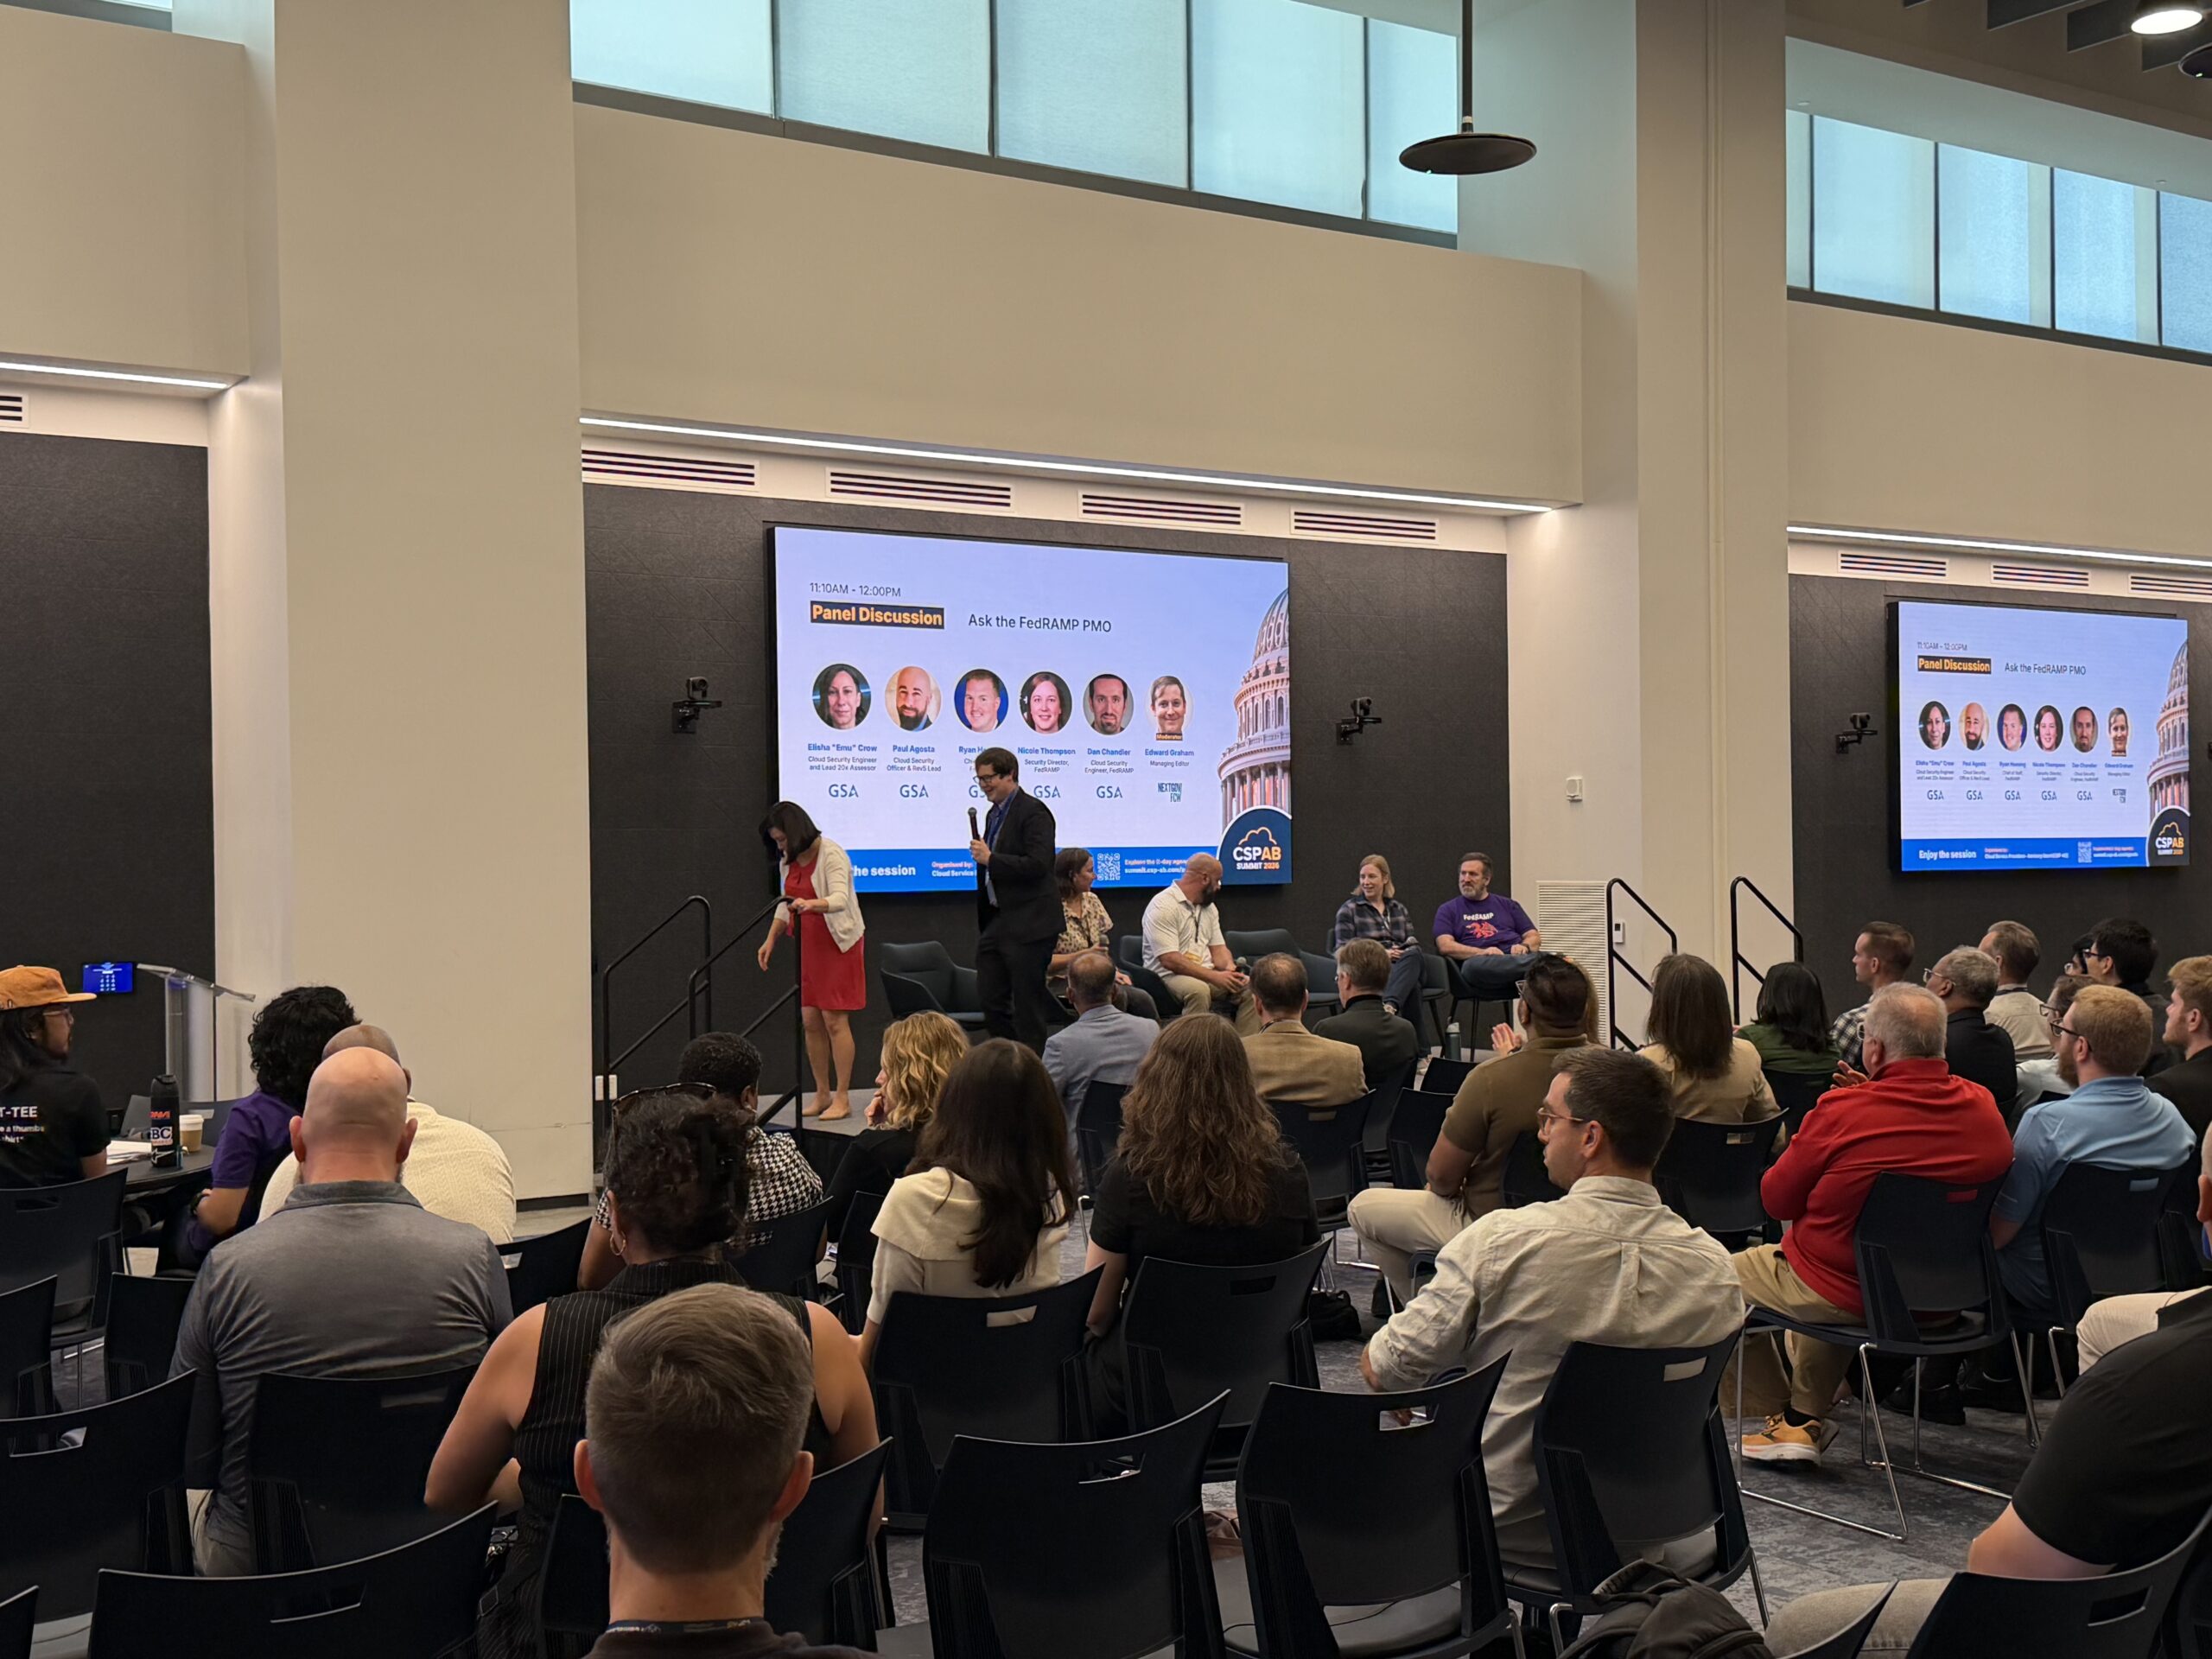
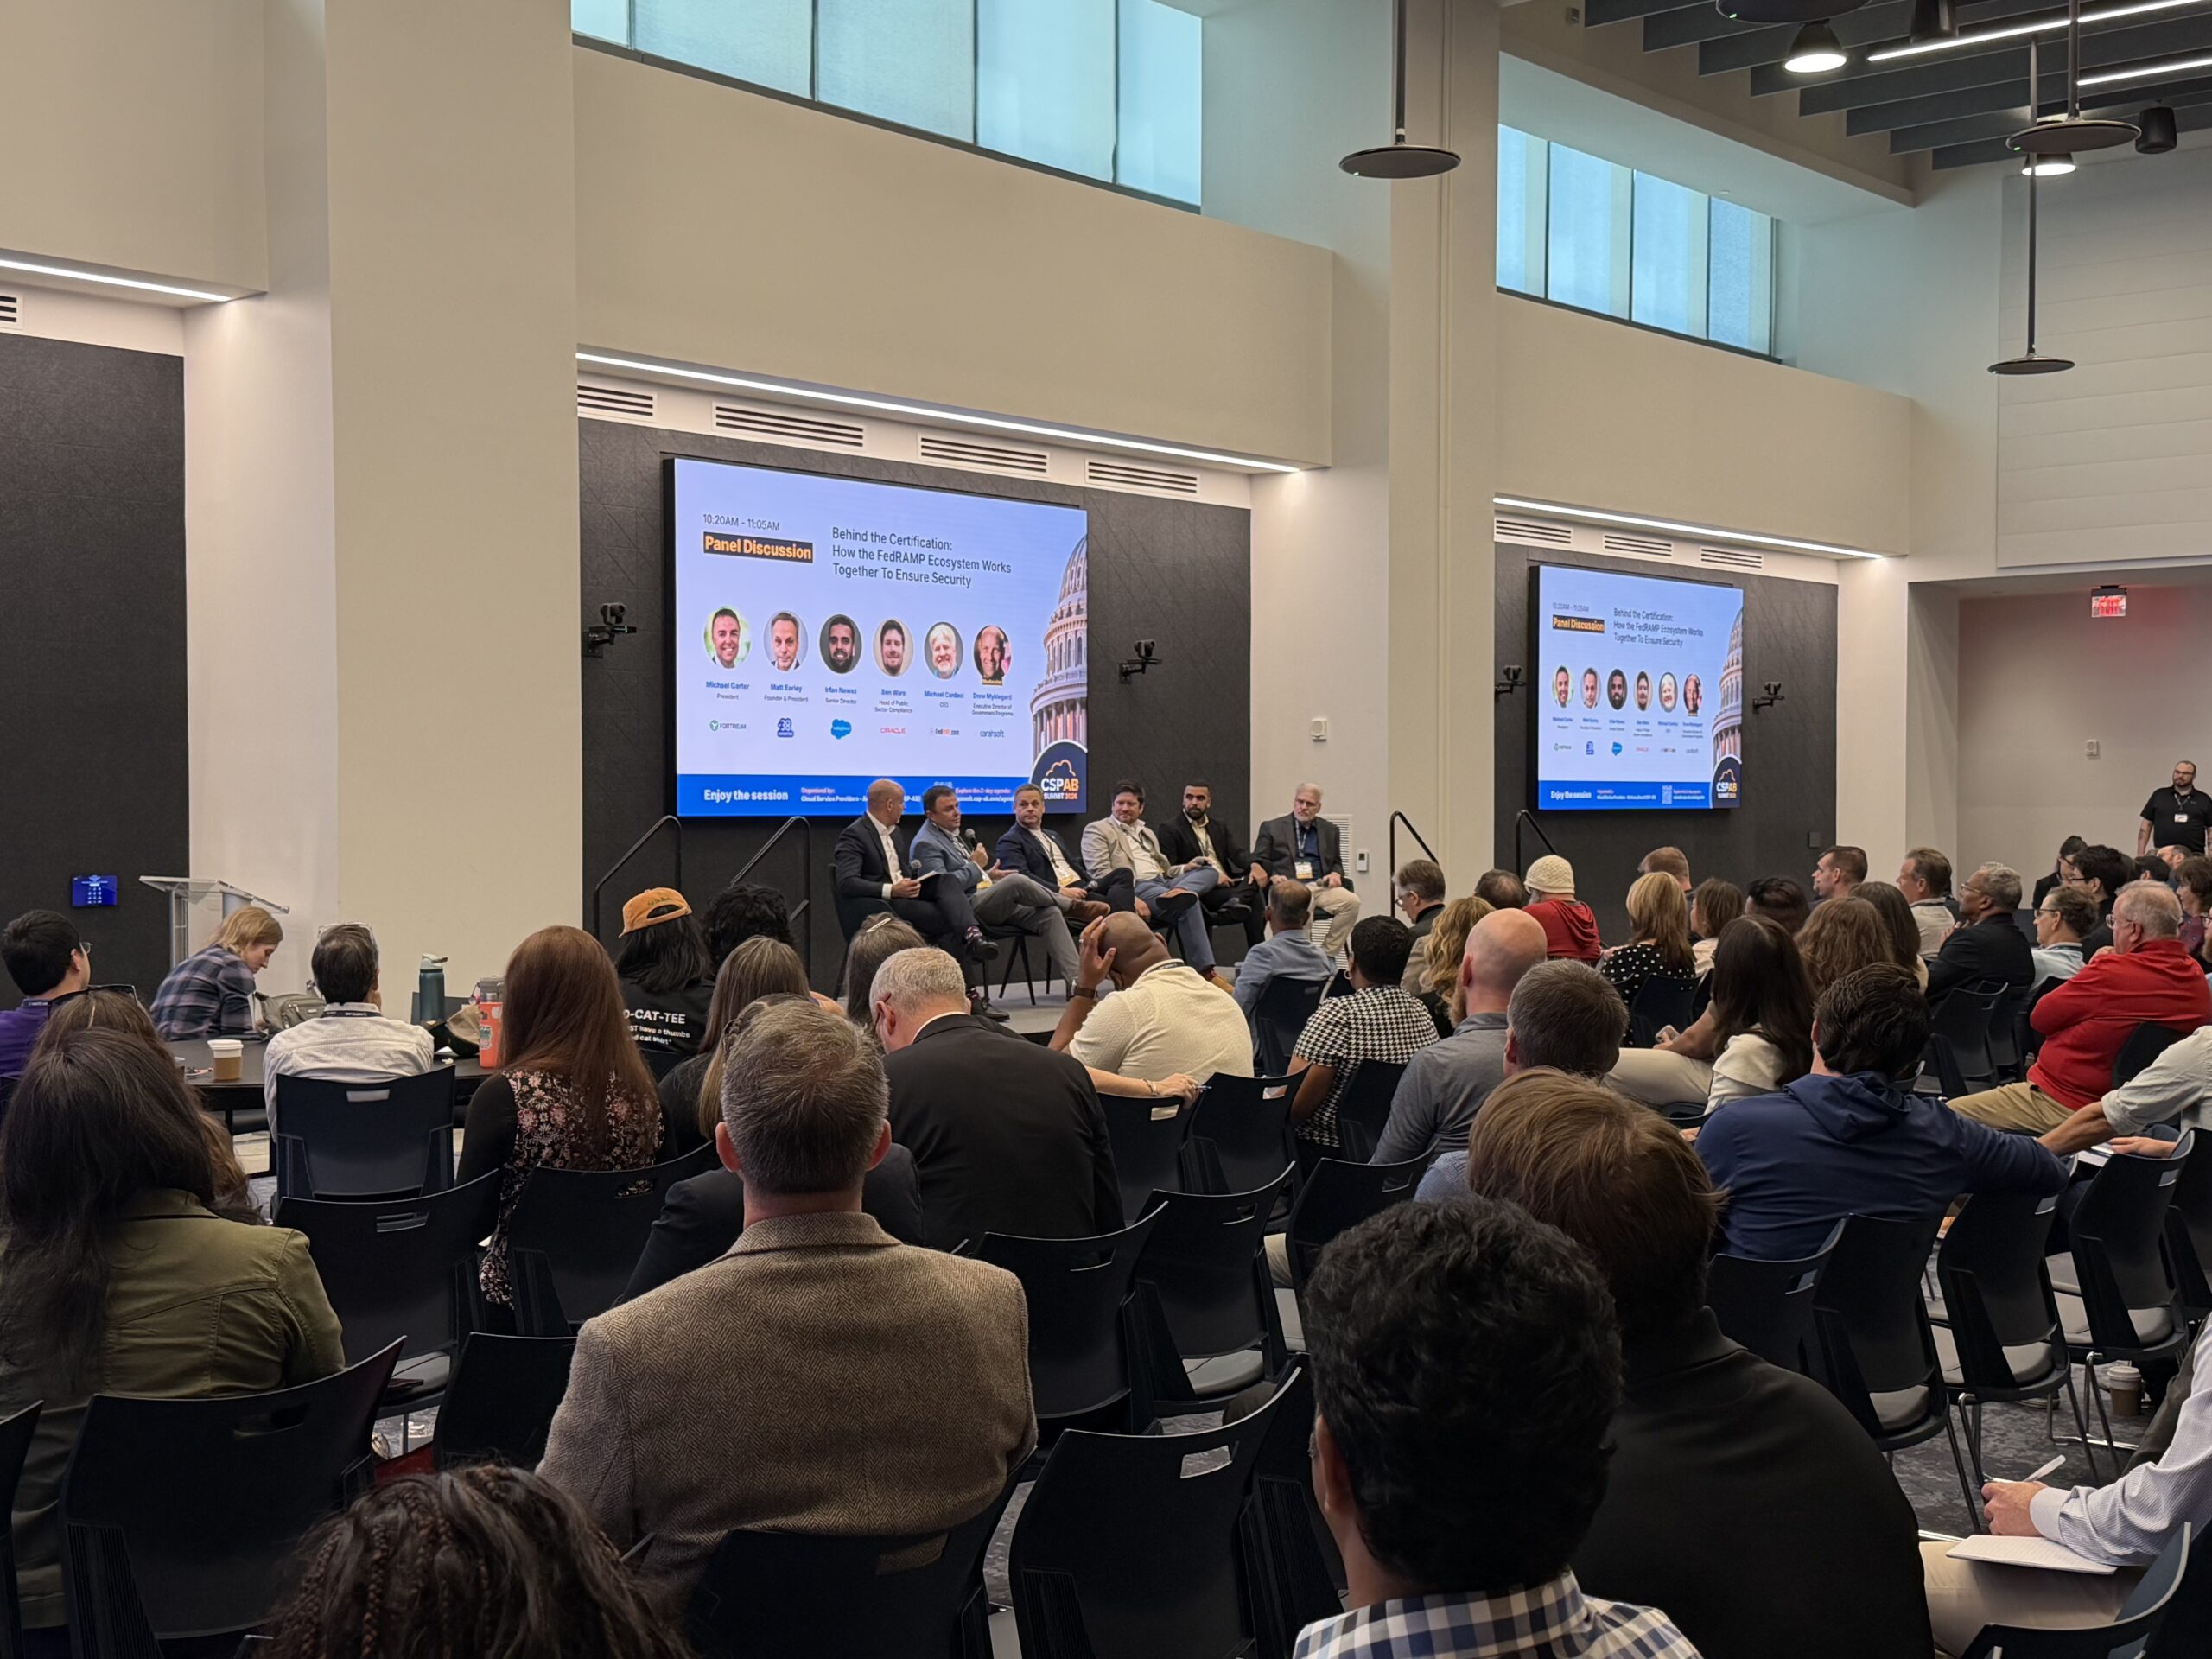
Day 2 was FedRAMP Day, which was open to both Federal employees and the broader FedRAMP stakeholder community for the first time. Sessions addressed the transition from Rev5 to 20x, how the FedRAMP ecosystem works together to ensure the security of cloud service offerings on the FedRAMP marketplace, and an Ask the FedRAMP PMO panel with key members of the FedRAMP team.
Among the themes that emerged across both days:
- Continuous security is the new standard. Point-in-time, manual documentation can’t keep pace with new and emerging cyber threats. Cloud service providers increasingly need to be able to demonstrate their security posture through continuous, machine-validated evidence.
- FedRAMP 20x depends on shared understanding. The shift is significant for cloud service providers and federal agencies alike. For it to work, the people who write the requirements, build the platforms, operate the systems, and assess and accept the risk need to be working from the same expectations, and in direct conversation with one another.
- Agency trust is built through transparency and a workable transition. As agencies and providers move from Rev5 to 20x, trust depends on clear expectations, consistent interpretation of requirements, and shared visibility into how security is demonstrated in practice.
- The conversations off the stage matter as much as the sessions. “The best conversations about cloud security and FedRAMP modernization don’t always happen from a stage. Sometimes, they happen in the middle of the crowd—surrounded by the agency and industry partners moving secure cloud adoption forward.” – FedRAMP PMO
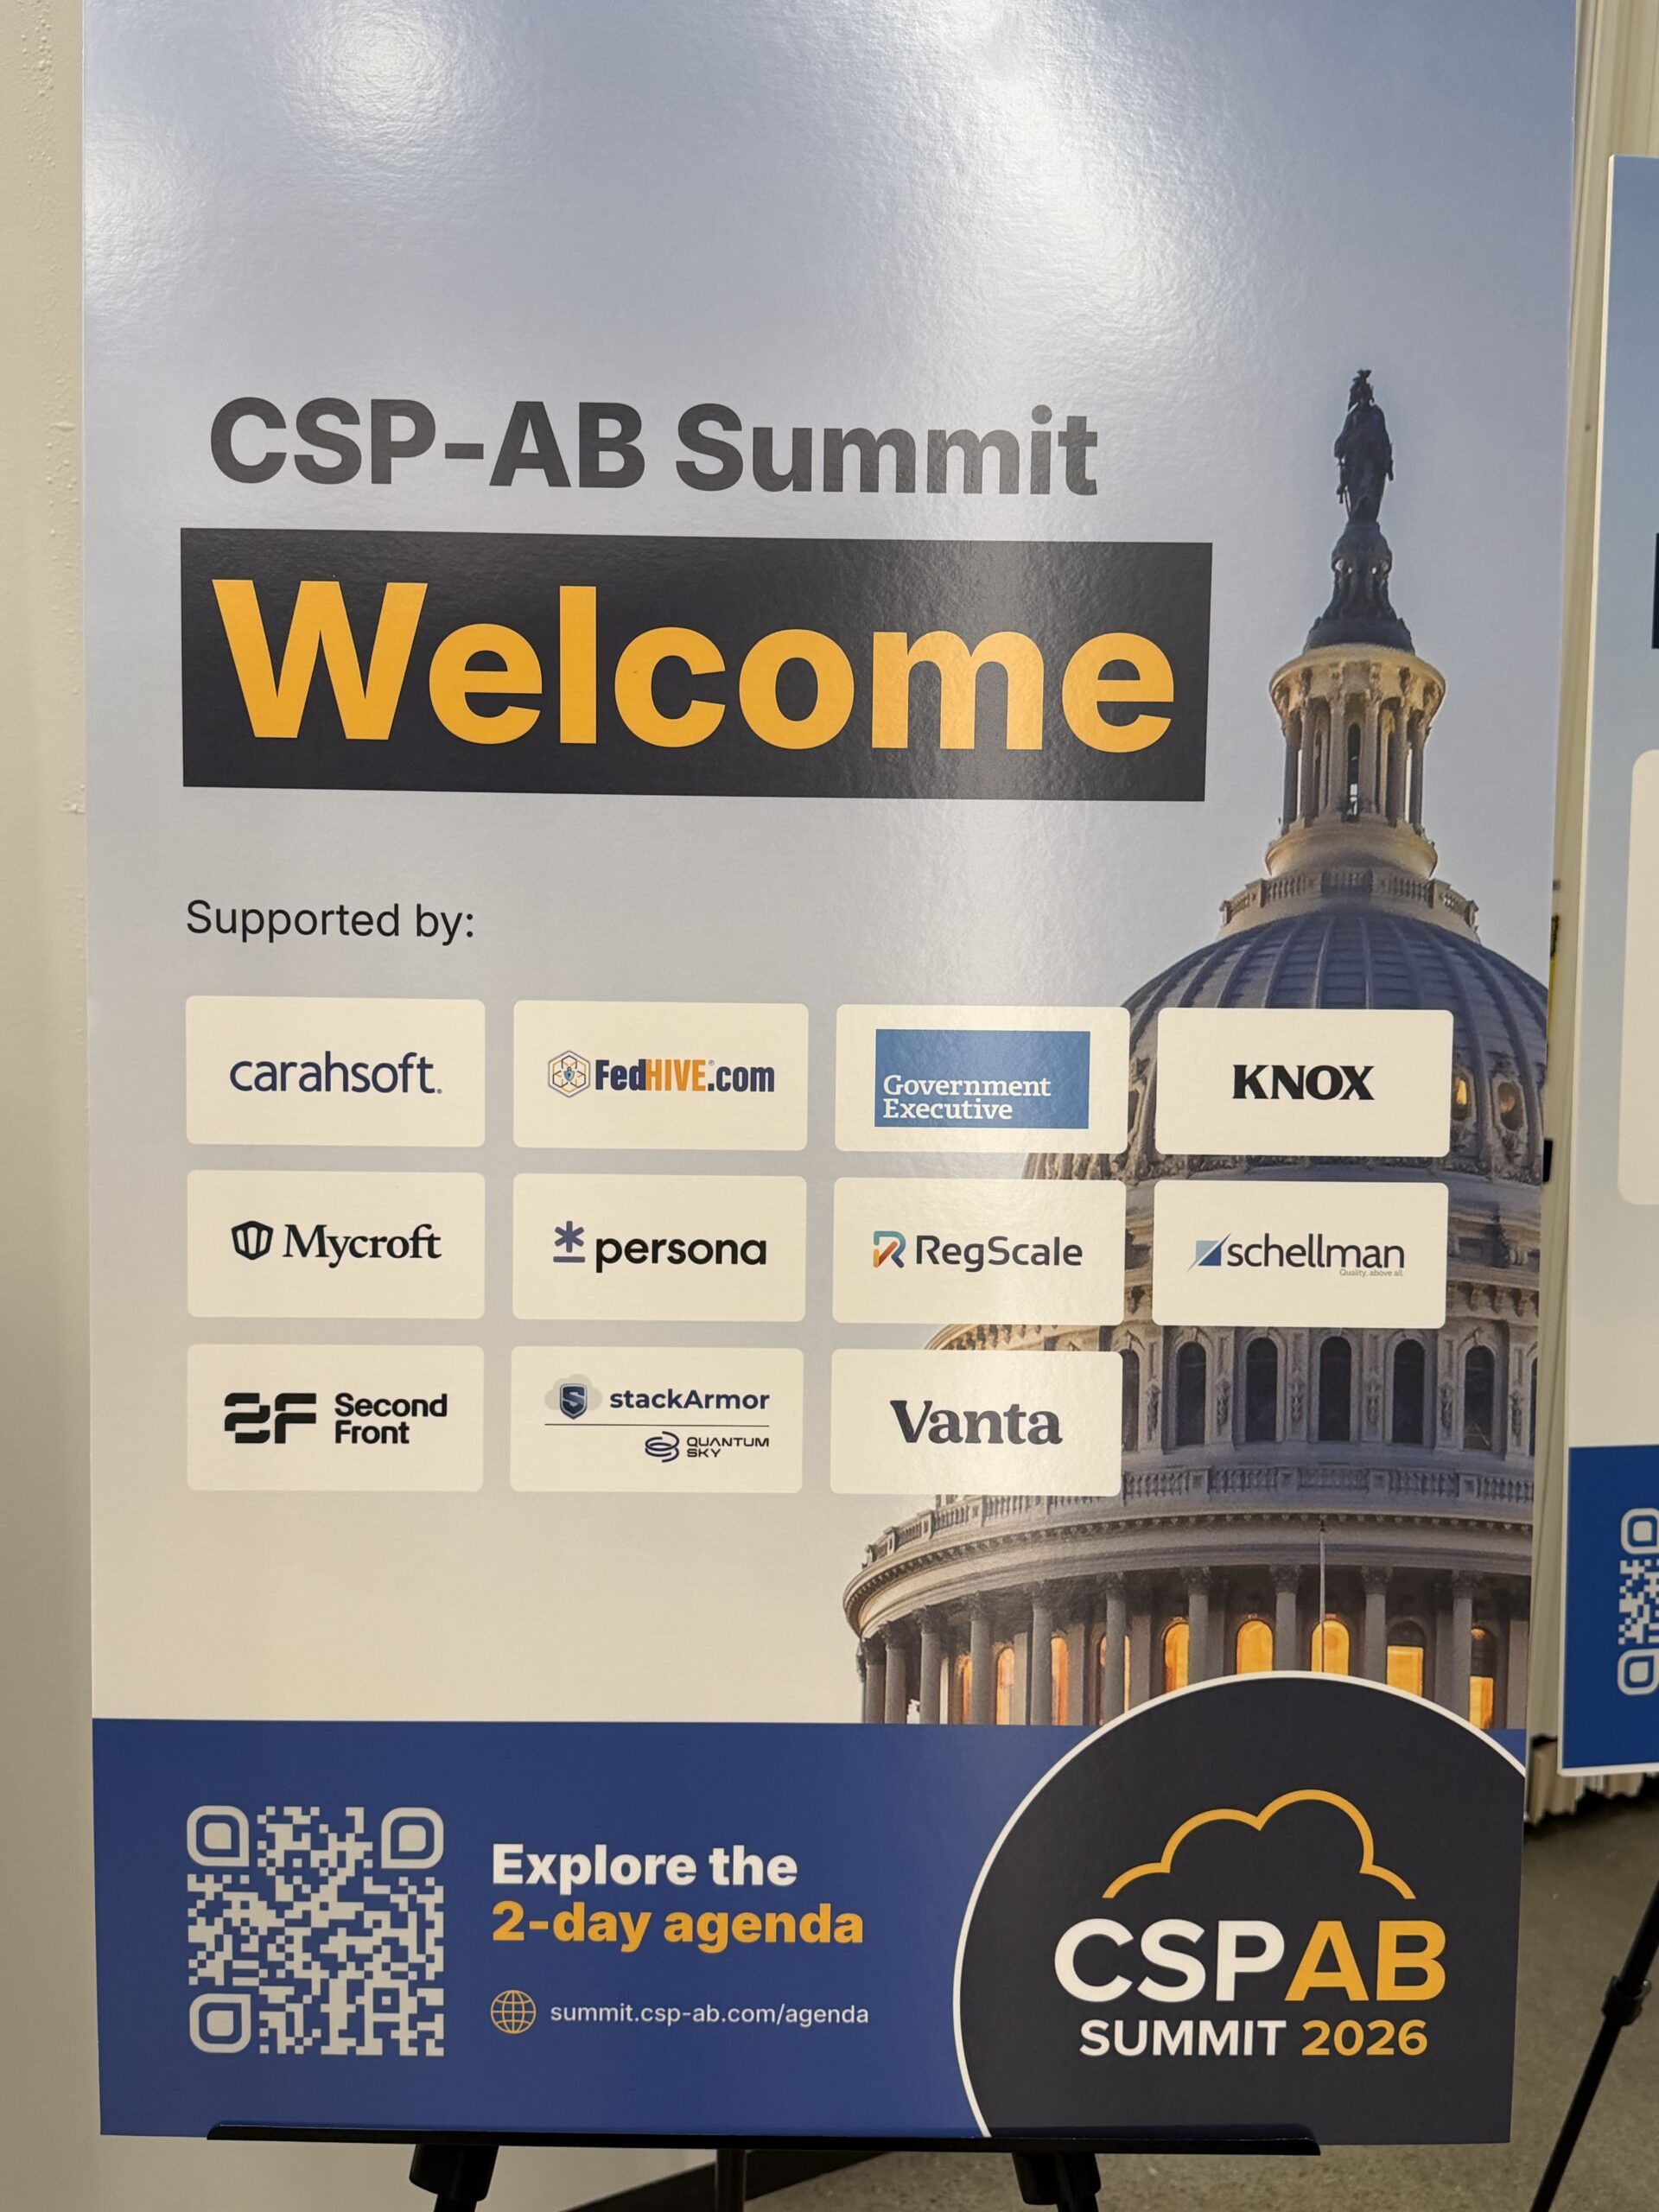
CSP-AB thanks its sponsors, speakers, panelists, and attendees who took part in making the 2026 CSP-AB Summit a great event.
CSP-AB plans to continue building on the conversation from the 20206 CSP-AB Summit by engaging with industry stakeholders, Federal agencies, and cloud security leaders on these important issues and will share more on its 2027 plans in the coming months.
About CSP-AB:
The Cloud Service Providers Advisory Board (CSP-AB) is a nonprofit trade organization representing leading cloud companies that serve federal government clients. CSP-AB seeks to advance standards and policies that promote secure cloud adoption in the public and private sectors.